

Table of contents of the article:
The climate is not calm and the current news that has just arrived regarding the Ukraine - Russia conflict which saw the invasion of Ukraine by the Russian army on the orders of President Putin, does not seem to reassure that there may be a term of the conflict soon. Rumors of economic and military support from NATO states with particular US involvement (Biden has already allocated a very first trance of 600 million dollars in arms for Ukraine in the immediate future), suggests that the affair could have escalated of violence with only 2 historical precedents, leading in fact to a real third world war.
This eventuality, which at first seemed absolutely unlikely, instead begins to take on the appearance of an eventuality that should not be underestimated and to begin to consciously evaluate.
Regardless of the economic and commercial relations with Russia that Italy has always supported, one cannot fail to keep in mind the obligations and duties that Italy owes to member states as a member and signatory of NATO agreements.
By virtue of this, as happened in other Middle Eastern conflicts in the run-up to the events of September 11th , Ad perpetuam rei memoriam, it is mathematically certain that if Russia's current show of force is countered by NATO, the member states must unanimously provide at the very least logistical, financial, and territorial support to NATO and its future war operations.
Assuming that we are limited to giving only support and not participating militarily in war actions that would make everything even more risky.
Having made the necessary premises and the ever-changing scenario being still indeterminable for now, we need to focus, at least for what concerns us from a professional point of view, to evaluate the room for maneuver for what could affect a cybernetic war or Cyber War between NATO countries. and Russia, or to begin to understand how to secure companies by re-evaluating some choices made in the past in which Italy / Russia relations were not as critical as they are currently (although Italy's moderation has now been demonstrated).
Uninstall Kaspersky Antivirus and related software solutions under their brand from all company workstations.
Kaspersky Lab ZAO (Лаборатория Касперского), commonly known as Kaspersky , is a Russian company headquartered in Moscow. Founded in 1997 by Yevgeny Kaspersky , it specializes in the production of software designed for computer security. Kaspersky Lab (/kæˈspɜːrski/; Russian: Лаборатория Касперского, Laboratoriya Kasperskogo) is a multinational cybersecurity and antivirus vendor headquartered in Moscow, Russia, and operated by a holding company in the United Kingdom. Kaspersky Lab develops and sells antivirus, internet security, password management, endpoint security, and other cybersecurity products and services.
On October 6, 2017, the Wall Street Journal – citing “multiple people familiar with the matter” – claimed that in 2015, hackers working for the Russian government used Kaspersky antivirus software to steal classified material from a home computer belonging to a National Security Agency (NSA) contractor. According to the report, the incident occurred in 2015 and remained unknown until early 2016. The stolen material reportedly included “details of how the NSA penetrates foreign computer networks, the computer code it uses for such espionage, and how it defends networks inside the United States.”[14] The New York Times reported that the hacks had been discovered by Israeli intelligence agents who had hacked into Kaspersky's network. On October 11, 2017, the Wall Street Journal further claimed that Russian intelligence was using Kaspersky software to scan computers worldwide for material of interest. The company again denied the reports, claiming they were "unfounded paranoia" and a "witch hunt," and found it suspicious that major US media outlets were simultaneously "attacking us almost in full force and simultaneously fantasizing, as if they were given an order, but they were confused about the details."
Kaspersky, therefore, suffered obvious consequences following this controversy over allegations of collusion with the Russian Federal Security Service (FSB): the U.S. Department of Homeland Security banned Kaspersky products from all government departments on September 13, 2017. In October 2017, subsequent reports claimed that hackers working for the Russian government stole confidential data from the home computer of a U.S. National Security Agency contractor using Kaspersky antivirus software . Kaspersky denied the allegations, reporting that the software had detected malware samples from Equation Group, which it uploaded to its servers for analysis during its normal operation. The company has since announced commitments to greater accountability, such as soliciting independent reviews and verification of its software's source code, and announcing that it would migrate part of its core infrastructure for foreign customers from Russia to Switzerland. In recent years, Kaspersky has received several accusations of collaboration with the Russian Federal Security Service (FSB), accusations that the company has always denied, requesting independent reviews and verification of its software source code and announcing the move of part of its software assembly infrastructure to Switzerland.
On November 13, 2017, the British intelligence agency MI6 raised suspicions about Kaspersky Lab software after it was distributed free of charge to over 2 million Barclays customers in the United Kingdom. On December 2, 2017, Barclays announced it would no longer provide the company's software to new customers. Also around December 2, 2017, the UK's National Cyber Security Center advised, as a national security precaution, that UK government departments avoid Russian-based antivirus software such as Kaspersky. On December 9, 2017, the United States government banned Kaspersky from civilian and federal military computers as part of a broader defense bill.
Less than a week ago, on February 22, Umberto Rapetto – an Italian general of the Guardia di Finanza, retired since 2012 and founder of the GAT (Anti-Crime Cybersecurity Group), which later became the Special Cyberfraud Unit – expressed his concerns about the use of a “famous Russian antivirus” by Italian government authorities in an article on Infosec.news https://www.infosec.news/2022/02/22/editoriale/in-tempi-di-guerra-la-nostra-difesa-ha-ancora-un-antivirus-russo/ .
It is worth mentioning an important passage from the article on Infosec.news:
Peering on the web we learn, in fact, that our Ministry of Defense would have been for years a valuable customer of a particularly well-established software house, whose indisputable technological capabilities have always been accompanied by some suspicion of possibly understandable proximity to the country of origin.
In 2018, the story of the ministries and public bodies that had bought the programs for the protection of their information systems from the Russian company Kaspersky came out. The company created, owned and directed by a great professional who graduated in Moscow in 1987 at the Faculty of Mathematics of the KGB High School boasted as clients the departments of Cultural Activities and Tourism, Defense, Justice, Infrastructure, Economy, Interior, Education, Development Economic, Agcom (the Competition and Market Authority), ENAV, CNR and the Central Directorate of Electoral Services ...
The request for "civic access" (taking advantage of the possibilities opened up by the so-called Italian Freedom of Information Act, which entered into force in December 2016) formulated by Euronews and the Hermes Center for Transparency and Digital Rights led to the drafting of an explanatory table that did not it has only administrative value but which can lead to reflections of a strategic nature.
Probably the repetition of a similar response - extended to all supplies whose "flag" origin could cause concern - would be a valid opportunity to detect potential risks and to adopt some late initiative in the best tradition that wants to close the stalls after the oxen have fled.
Having to necessarily take into consideration the above premises, it seems clear and obvious, in compliance with the precautionary principle ( and therefore only as a precaution in the absence of direct accusations and specific evidence ), to avoid purchasing Kaspersky branded solutions and to immediately replace them with alternative software such as Avira, BitDefender, GData or NOD32, respectively German, Romanian and Slovak solutions , of which we recommend the excellent BitDefender according to statistics and data from independent laboratories.
Someone will read with extreme amazement that there have not been cited brands of excellence and noble as McAfee, Norton, Checkpoint.
It is not an oversight, but the wise choice to choose only and exclusively European software products and not those controlled by foreign holding companies and/or at least non-EU interests.
Although there is no regulation on this nor any obligation in what is the regulation of the European Union better known as GDPR it is always recommended to use where possible and replaceable European production software. This should be the practice for what concerns government and ministerial offices and instead unfortunately there is still a legislative hole in this regard that we hope will be filled following current events.
Filtering connections from Russia at the network and application level
Although this operation can be postponed to a more critical diplomatic situation, it is already necessary to take into account the need to filter the connections (and any attack attempts by Russian IPs).
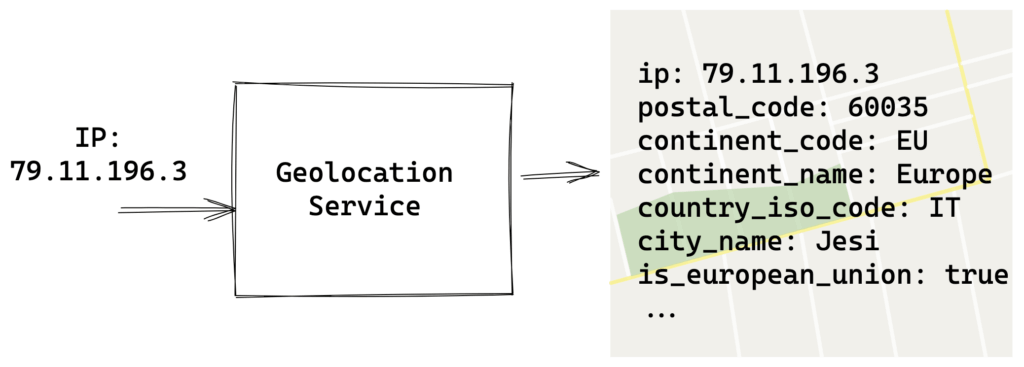
All this can be done by the company CTO who will draw up a plan with related technologies to provide for the filtering of Russian connections, relying on Geo IP Geolocation (through, for example, MaxMind technology) which allows you to trace the origin of a IP network connection
For those who want a more streamlined approach at the SOHO (Small Office Home Office) level, you can opt for Free solutions such as CloudFlare filtering.
It would be useful, for example, to block requests from Russia with a CAPTHCA (or completely block for Italian institutional and government sites).
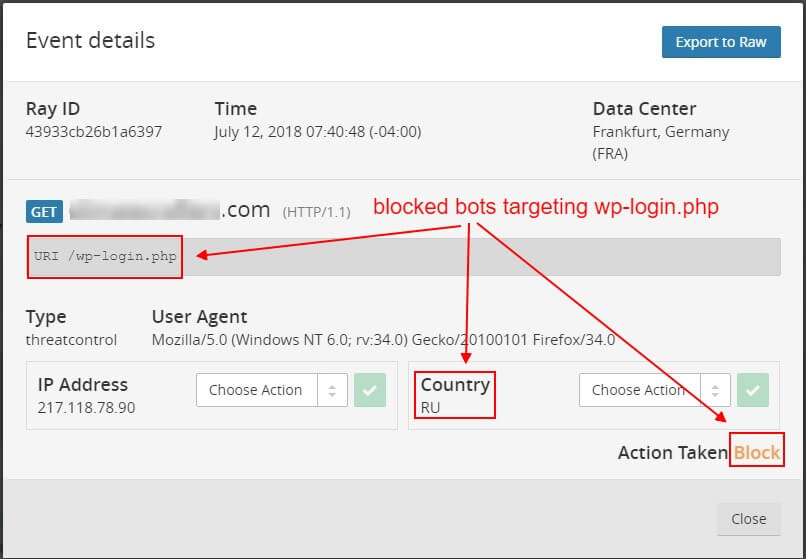
We've discussed CloudFlare in depth in this article: DDOS attacks and Bitcoin payment extortion? How to protect yourself with CloudFlare . It's currently the fastest and most immediate solution for implementing a significant incoming connection filtering system at a low cost (if you're familiar with it, it's practically free).
Use NGINX Web Server only from the version after the acquisition of F5
NGINX Inc. is the support and consulting arm of an open-source reverse proxy web server project that is very popular with some of the world's highest-volume internet services. The company is of Russian origin but was sold to F5 Networks in 2019. The company's founder, Igor Sysoev, announced his departure in January of this year.
Considering the growing trend of NGINX Webserver (which is for example at the heart of our high performance Hosting infrastructure), it would be advisable to update NGINX to the latest version, (or in any case recent at least by 2021) possibly opting for recompilation from source, rather than from binary packages from repositories like yum or apt.
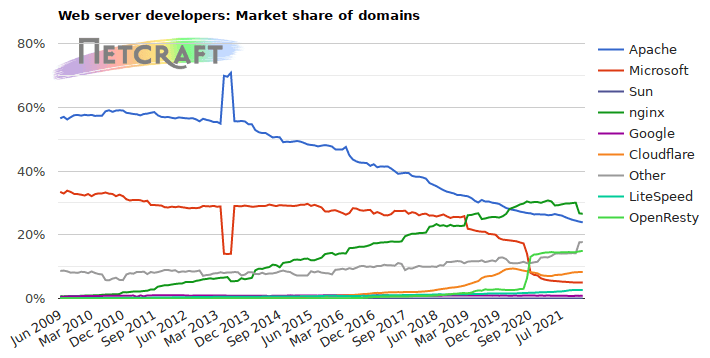
It is worth mentioning the strange case of the Russian police raiding the NGINX offices in Moscow in order to be able to make some considerations regarding the risk that was run until NGINX was acquired by the US company F5 for about 600 million dollars. .
On December 12, 2019, Russian police broke into Nginx's Moscow office, arrested company employees, original developer Igor Sysoev, and another co-founder Maxim Konovalov.
The searches are due to complaints filed by Rambler Group against NGINX. Rambler claims that Sysoev developed the open source Nginx web server when working as a system administrator in Rambler.
The Nginx web server was released publicly in 2004, is free, open source software, and can also be used as a reverse proxy or load balancer.
Igor Sysoev said he developed Nginx “ with the goal of overcoming some of the scaling barriers of web infrastructure difficulties in handling many concurrent connections, reducing latency, and offloading static content, SSL, and persistent connections .”
Nginx, Inc was formed in the year 2011 with the aim of providing support and providing Nginx plus paid software. In 2019 NGINX was acquired by F5 Networks for $ 670 million. According to the w3techs report, Nginx is used by over 30% of websites, including Gainst like Facebook, Netflix and Apple.
The Rambler Group claimed that Igor Sysoev began developing NGINX when he was an employee of Rambler Internet Holding; therefore, “ any use of this program without the consent of the Rambler Group is a violation of exclusive rights .”
Igor Sysoev stated in an interview with Hacker magazine in 2012 that he developed NGINX in his spare time while working at Rambler, he also said that "programming was not part of my job responsibilities at Rambler".
Rambler also claimed that Sysoev worked on the Nginx project during working hours; then, he distributed the web server software for free on the Internet, later the property rights of Nginx Inc. Rambler said this deal and free distribution are illegal and cost an estimated damage of 51,4 million rubles ($ 820.000 ).
According to a Forbes report , the case was dismissed under Article 146, Part 3, which carries a six-year prison sentence with fines of up to 500.000 rubles.
Backup and Disaster Recovery
Although it must already be a tested and consolidated practice also on the basis of the directives in force and the former DPS (Programmatic Document on Security) - now abolished - it must always be remembered that a Backup and Disaster Recovery procedure is an added value both for the individual and for the company. Regardless of the size of the company that will use based on the available budget of professionals in the field of data security, we recommend that all companies of any size use at least basic Backup and Disaster recovery solutions and possibly if the connection allows (at least 20 megabits in Upload) to use Cloud solutions rather than physical backups in the company. Better if both with double security copy.
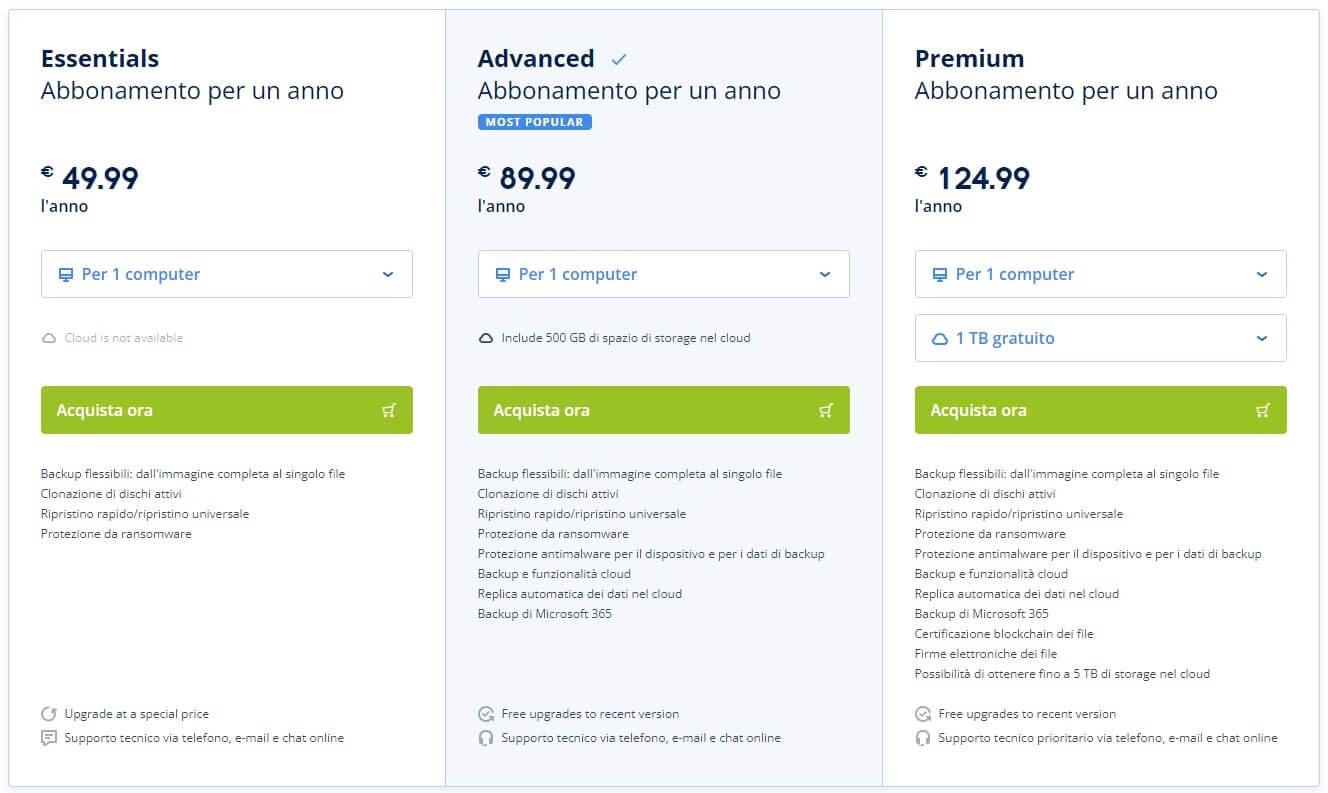
For small and medium-sized companies, a suitable solution could be that of Acronis.
Acronis Inc. is a software company headquartered in Burlington Maryland and several smaller offices in Asia and Europe. The company is known for software systems that enable backup and disaster recovery for both a business and home market.
Its strength lies in its offering of integrated cyber protection, along with disk image creation for backup and recovery, partition and management, boot and management, data and entire system migration, and data deduplication. It also develops virtualization software for migrating a physical server to a virtual server (such as VMware), also known as P2V. Its best-known product is Acronis True Image, which allows you to create an image of a computer that can be reinstalled on the same or another machine.
Acronis provides "turnkey" solutions for companies of any size and any budget (starting from 90 € / year for Cloud solutions) and unlike other cutting-edge products such as VEAM for example, it does not need to have other interlocutors and suppliers to remote cloud storage management. It is therefore suitable for small / medium-sized companies that want to have a solution that is now the market leader, quick, fast, balancing a low cost with a high added value.
Good advice but not only in times of war.
These are the basic tips that every company should take into consideration in view of possible attacks, and not necessarily attacks derived from the current war climate, but from those that arrive every day on the connection of your company and your site without them. give the slightest account.
How many cyber security attacks are there every day?
A Clark School study at the University of Maryland found that 2,244 attacks occurred every day which is almost 1 cyber attack every 39 seconds.
A study by the Australian Government's Australian Cyber Security Center (ACSC) found that an average of 164 cybercrimes per day or about one every 10 minutes.
What is the most alarming security problem on the internet today?
Ransomware is the number one cybersecurity threat in 2021. Ransomware is one of the most dangerous types of hacks because it is relatively easy and cheap to execute and because it gives cybercriminals the ability to deny access to computer files until a ransom is paid.
How many cyber attacks happened in 2020?
A study by Arkose Labs estimated that by August 2020, there were 445 million cyber attacks globally, double the number for the whole of 2019. Cybercrime is reaching an all-time high, and there are expected to be nearly a billion attacks globally this year.
Where do most cyber attacks come from?
Russia, Brazil and China are the top three countries where cyber attacks originate.
Russian hackers tend to target banks in the US and Europe. Since the XNUMXth century, the Russian education system has encouraged the pursuit of scientific knowledge and curiosity in its students, which has had the side effect of favoring cybercriminals.
Brazilian hackers typically use simple Russian-inspired tactics that have little exposure risk. Hackers in China send mass text messages in an attempt to coerce victims into fraudulent transfers.
How long does it take for cyber attacks to be detected?
On average, it takes about 280 days to detect and stop a cyberattack. A typical organization takes about 197 days to identify a threat, but some breaches can go undetected for a long time. The time it takes your company to remove a threat depends on the robustness of your security system.
Once detected, an attack often persists for an average of another 69 days. Companies that can subdue attacks in less time can save hundreds of thousands of dollars in recovery costs.
Russian utility companies will also be affected
Many global technology giants in the software and services industries have used Russian and Eastern European developers in the past due to their high-quality, affordable work compared to their US and Western European-based counterparts. And many have invested hundreds of millions of dollars to have a developer as well as reseller channel presence in Russia.
World governments do not need to impose Iran-style isolationist sanctions against Russia for a snowball effect to begin within US companies that use Russian software or services.
The escalation into a full-blown conflict in Ukraine will make C-seats within global companies extremely concerned about using software originating from Russia or produced by Russian citizens. More conservative companies will likely "rip out and replace" most standard features and choose other solutions, preferably American ones.
Russian mobile apps? BYOD mobile device management (MDM) policies will prevent them from being installed on any device that can access a corporate network. And if sanctions are put in place by world governments, we can expect them to disappear completely from mobile device stores.
Countless games and apps from Russia may no longer exist when effective sanctions are implemented on that sector.
But C-seats won't wait for governments to ban Russian software. If there's a lack of trust in a vendor's reliability, or if there's a fear that its customers' loyalty could be compromised or influenced by Putin's regime and used to compromise their systems, you can be sure that Russian-sourced software will quickly disappear from corporate IT infrastructure.
Contractor visas will surely be canceled en masse or not renewed for Russian citizens doing jobs for large corporations. You can count on it.
Any vendor being considered for a large software contract with a US company will undergo a thorough check and will be asked if any of their products involve Russian developers. If it does not pass the most basic audits, they can simply forget about doing business in this country.
So if a vendor has a major Russian developer workforce, they'll have to pack up and move those labs to the US or a country that's better aligned with US interests, as we've seen with the companies listed above. This is especially true for anyone who wants to do federal contract work.
Then there is the issue of custom code produced by outsourced companies. It gets a lot more complicated.
Obviously, there is the question of how recent the code is and whether or not there are adequate methods to verify it. We can expect that soon there will be service products offered by US and Western European IT companies to sift through huge amounts of custom code so that they can be sure that Russian citizens leave no compromises under the influence of the Putin regime.
If you thought your Y2K mitigation was expensive, wait until your company experiences the Russian Purge.
I don't have to tell any of you how expensive this proposal is. The wealthiest companies, sensing a huge risk to customer safety and trust, will address this issue as quickly as possible and swallow the bitter pill of expensive audits.
But many companies may not have the immediate funds to do so. They will do their best to mitigate the risk on their own, and the compromised code could stay around for years until major system migrations occur and the old code is (hopefully) eliminated.
We will almost certainly be dealing with Russian cyber attacks from within the walls of our own companies in the years to come, from software initially developed under the aegis of having access to talented, strategically outsourced, relatively cheap and highly skilled programmers.
Will Russian software and services become the first victim of a digital war?

