

Table of contents of the article:
Introduction
In March, we received reports from one of our clients, laleggepertutti.it , who was complaining about fraudulent clicks and related payment deductions by advertising agencies.
We investigated with no little difficulty, leaving the task pending for about a week in order to enable a more detailed logging system and collect more data than the standard ones and better understand the problem complained of by the customer.
A second report from another of our clients, webmaster Matteo Morreale of Jablabs.it, was a godsend . He was complaining about the same issue described above. Thanks to his collaboration, we were able to cross-reference data and perform a differential analysis, pinpointing the problem in great detail and even identifying the source IP addresses responsible for the fraudulent clicks on the respective sites' ads.
Daily analysis
The analysis carried out revealed that an IP class in the range 176.126.83.0 – 176.126.83.255 was the incriminating one and the author of the fake clicks, most likely through the aid of bot systems or equivalent automations.
The IP class in question as reported by the following whois:
% Information related to '176.126.83.0 - 176.126.83.255'% Abuse contact for '176.126.83.0 - 176.126.83.255' is 'info@oneprovider.com' inetnum: 176.126.83.0 - 176.126.83.255 netname: OneProvider descr: OneProvider country : IT org: ORG-OA765-RIPE admin-c: CP10803-RIPE mnt-domains: dagroup tech-c: CP10803-RIPE status: ASSIGNED PA mnt-by: dagroup mnt-by: ONEPROVIDER mnt-by: MNT-SEFLOW created : 2016-07-21T17: 32: 21Z last-modified: 2016-12-01T21: 19: 31Z source: RIPE organization: ORG-OA765-RIPE org-name: ONEPROVIDER org-type: OTHER address: 1500 Ste-Rose, H7S 1S4, Laval, Canada abuse-c: ACRO410-RIPE mnt-ref: WILLIAM-MNT mnt-ref: dagroup mnt-by: ONEPROVIDER created: 2016-03-07T23: 08: 42Z last-modified: 2017-02-03T15 : 51: 44Z source: RIPE # Filtered person: Charles-R Paquet address: 1500 Ste-Rose, H7K 1S4, Laval, Canada phone: +1.5142860253 10803 nic-hdl: CP2016-RIPE mnt-by: ONEPROVIDER created: 08-04-12T08: 28: 2016Z last-modified: 09-22-13T12: 59: 176.126.83.0Z source: RIPE% Information related to '24/49367AS176.126.83.0 'route: 24/49367 origin: AS2016 mnt-by: SEFLOW-MNT mnt-by: MNT-SEFLOW created: 08-04-22T45: 27: 2016Z last-modified: 08-04-22T45: 27: XNUMXZ source : RIPE
It belongs to OneProvider , a Canadian hosting provider present in several continents such as Europe which deals with the supply and rental of hosting services, dedicated servers and cloud.
Specifically, if we examine the previous whois in more detail, it emerges that the class, although assigned to OneProvider, is managed at the transit level (Transit ed.) or connectivity provider, by an Italian provider in Cologno in the province of Lodi called SeFlow.
Obviously we contacted the Italian connectivity provider SeFlow complaining about fraudulent activity from IPs that had references to their hosting company , submitting a certified email and receiving in response what we had already deduced from the previous whois.
Dear Marco,
thank you for contacting the SeFlow SOC department.The IP addresses indicated by you are not in use by SeFlow. As you can see by querying the RIPE database,
https://apps.db.ripe.net/db-web-ui/query?searchtext=176.126.83.250
the owner company is One Provider (at the link below you can find the references)https://apps.db.ripe.net/db-web-ui/lookup?source=ripe&key=ONEPROVIDER&type=mntner
SeFlow (among the many IP Transit companies they have) is just one of their connectivity providers.
We therefore invite you to communicate the abuse to One Provider, a usufructuary company and owner of the IP addresses indicated by you.We remain at your disposal for any clarification
Yours sincerely
Click fraud solution
Although we reported the issue to OneProvider and had no intention of waiting for their response (which never arrived, by the way) which could have opened hypothetical scenarios of legitimacy or otherwise of the request on a Canadian hosting provider, not Italian or even European (the activity of fraudulent clicks is in fact of dubious interpretation due to the lack of a specific legislative reference that has global value) we decided to take action to ban the IP class '176.126.83.0 – 176.126.83.255' at the server level using the very common iptables (the default firewall of GNU/Linux systems) free and present in all distributions of the well-known Open Source operating system.
The syntax is really very simple, and it was enough to issue the following command from the linux shell (and with root privileges), to see all the traffic of that range blocked:
iptables -A INPUT -s 176.126.83.0/24 -j DROP
The syntax is obviously specific to GNU/Linux systems but technically the same approach, albeit with different commands and syntax, can be applied using any hardware or software firewall and any operating system.
Solution for uncooperative hosting providers.
It is necessary to premise that although this command can be given without any problem on any vendor that grants you the ability to manage a Firewall, or any dedicated instance with administrative privileges (root in the case of GNU / Linux systems), it can present big but not insurmountable difficulties if the site victim of fraudulent clicks is hosted in a shared hosting (shared hosting) that unites in a single server many other customers as well as your site.
It is undisputed (although questionable) to say that blocking a range of IPs at the server level (therefore not only for your site but also all the others hosted on the same server) can be interpretable and subject to discussion, as what could be good for one customer it doesn't necessarily have to be for everyone else.
Many suppliers could in fact trash your legitimate request, with a more than legitimate motivation by appealing to net-neutrality rather than to a less professional and less motivated "laziness".
However, if you decide not to migrate your site to another hosting provider that can guarantee the introduction of specific firewall rules to block this type of fraudulent activity, you can always use specific solutions for the web server that will allow you to block the offending range, for example using .htaccess rules for Apache or LiteSpeed web servers.
To block the specific range, add the following to your site's root .htaccess file:
Deny from 176.126.83.0/255.255.255.0
If you use another webserver such as NGINX you will necessarily have to use your Hosting Provider or the features present (if enabled) in some control panels such as Plesk / cPanel / Directadmin (to name the most famous) and apply the block of the range .
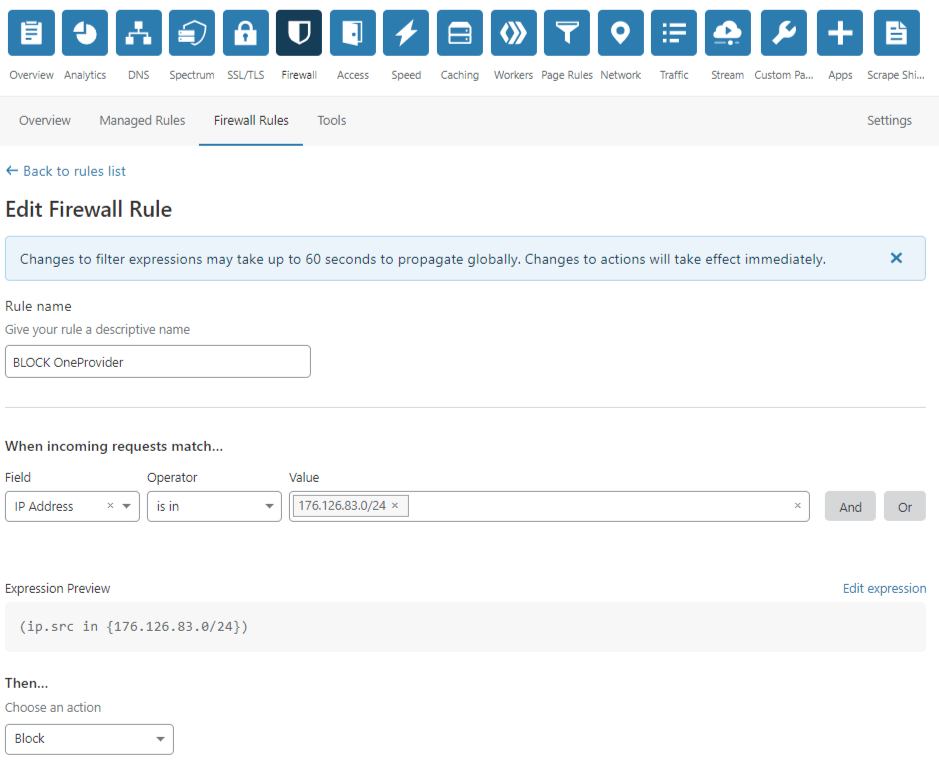
For those who use CloudFlare or intend to do so, you can apply the rule directly from their control panel in the Firewall section and then Firewall Rules in this way:
In short, the solutions can be very varied and essentially linked to the type of system you have and the related skills in implementing the blocking of IP authors of fraudulent clicks.
In case of doubts or hesitations, the assistance of qualified technical personnel will certainly put you in a position to operate safely in order to avoid problems deriving from a bad implementation of the filtering rules.
Some considerations on this.
Until now we have spoken in absolute and unobjectionable technical terms, however we feel entitled to hypothesize what may be the reasons for this fraudulent activity to the detriment of advertisers and publishers who find themselves important cuts on the monthly payouts of the dealerships.
What follows therefore are personal considerations, dictated by common sense and by reasoning as logical as possible aimed at identifying the motive for this fraudulent activity.
Given that having a server structure with a class C of dedicated IPs involves an economic investment, albeit not very high (we are in the order of a few hundred dollars) but in any case not free, one wonders what is the personal advantage of those who invest resources money and their time to set up bots that fraudulently click on the ADS of customer sites.
Considering that there is no way to obtain a direct economic advantage from this activity, it is common ground that the advantage obtained can instead be indirect.
One of the reasons, in fact, could be that of a strategy to generate discontent in the owners of websites that seeing significant sums cut in the monthly payout (even over 50%) in the item "Invalid traffic", could entice the site owner to pass to alternative advertising circuits.
In fact, it can be an alarm bell to receive a spontaneous proposal from some alternative advertising circuit following one or two months of fraudulent clicks.
It certainly wouldn't prove direct involvement in the fraudulent click generation activities, but it would leave room for reasonable, albeit merely circumstantial, suspicions about what might have happened and how the apparent way out was actually part of the trap itself.
A real example on one of our clients
Here, for example, is what happened to Anna between May 10 and 11, 2021 (full identity has been censored for privacy reasons) who saw her blog, which has over 1,5 million visitors per month (and deals with medical topics), bombarded by clicks on Google Ads, to the point of not monetizing and seeing her Google advertising account suspended.

The content of the request was absolutely alarming as the customer was soon unable to continue the monetization of genuine traffic, spoiled by false clicks on Google banners (Click Fraud) and therefore seeing herself undermining a business that had hitherto been serene. and flourishing.
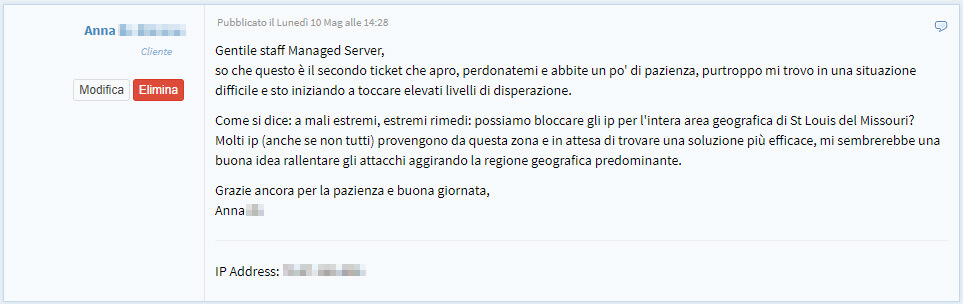
Obviously we understood the suggestion of the customer who, even if with non-technical skills in the field of networks and the Internet, certainly had guessed at least the logic in protecting herself.
We have therefore proposed an adequate solution by proposing an important value-added service that we offer to our customers.
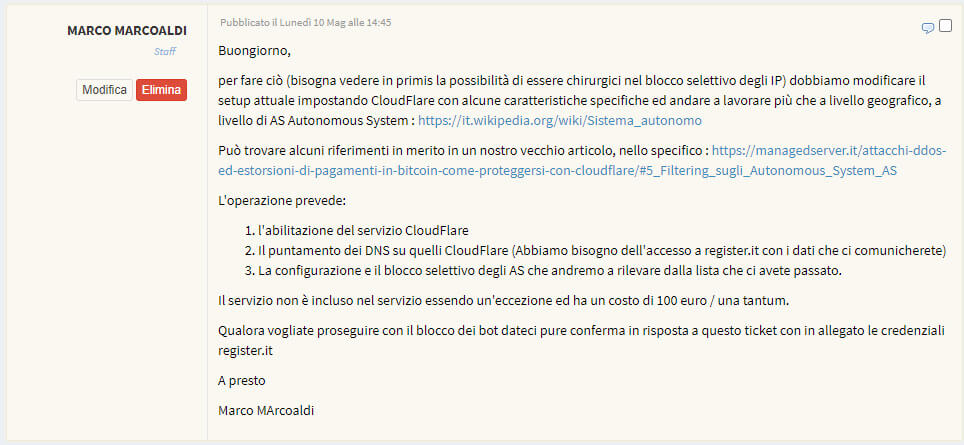
We worked by implementing several rules on the Web Application Firewall, creating a "selective combo" in order to filter real traffic from bot traffic in an extremely selective way due to false clicks.
After some reinterpretations and changes to the rules, we invited the customer to test after a few hours the effective quality of the filters put into production and the solution of the problem.
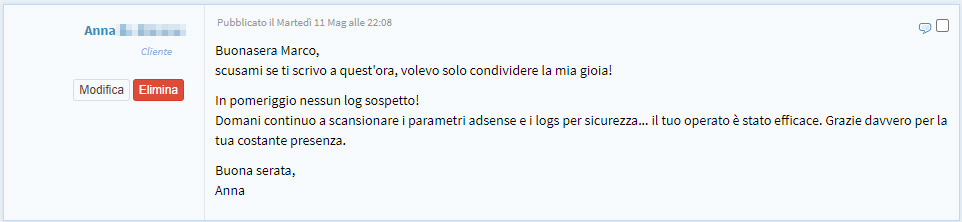
The customer answered us late in the evening sharing the joy of finally seeing this ugly attack ceased to the detriment of his serenity and his business.
It is obvious that beyond the mere economic return for our service, seeing satisfied and rejoicing a customer is something priceless.
Conclusions
Regardless of what may be the real reasons for the fraudulent click activities that are bombarding your site, reducing not only your monthly payout but also your personal peace of mind, our advice is to stop the problem by blocking the IPs that refer to the range indicated above.
Blocking any fraudulent activity against you means not only applying the best solution for yourself but also for all website owners who, unaware of the phenomenon, continue to be silent victims of these activities, which certainly deserve to be condemned at least on ethical and moral grounds. Hopefully, with the collaboration and synergy of all those involved, both insiders and outsiders, we can finally eradicate this currently little-known problem.

