
Table of contents of the article:
When a WordPress site is hacked, the first thought is almost always the same: find the vulnerability, remove the malware, restore the compromised files, and get the site back online.
It would seem like a linear procedure.
The site is compromised, it is cleaned up and the problem is solved.
Unfortunately, in reality, it doesn't always work that way.
In some cases, the real emergency begins precisely when the site has already been technically cleaned , because during the compromise period the domain may have ended up in the reputation databases used by antivirus programs, telephone operators, and secure browsing services.
And being blacklisted can be a matter of hours.
Getting out of it, however, can take days or even weeks.
At Managed Server Srl, we have developed a methodology and procedure that, after cleaning the website (i.e., ensuring it is not infected), allows us to resolve the blockage within 24/48 hours on weekdays. (Contact us to resolve the issue.)
This is exactly the problem we recently found ourselves dealing with on an Italian clothing e-commerce site based on WordPress and WooCommerce.
The site had been entrusted to the Webmaster for application management and, in all likelihood, some important update to WordPress, the theme, or one of the installed plugins had been postponed or skipped.
The result was what we unfortunately see quite frequently: a vulnerability exploited by attackers, the site compromised, and subsequently detected by automatic security systems on the Internet.
The cleanup fixed the issue on the server.
But not that of reputation.
And for an e-commerce site that generates revenue every day, this difference can become extremely costly.
The site is clean, but many users still don't log in
The situation may initially seem incomprehensible.
The server is responding correctly.
WordPress works.
WooCommerce works.
The HTTPS certificate is valid.
DNS resolves correctly.
The malware has been removed.
Orders can be placed as normal.
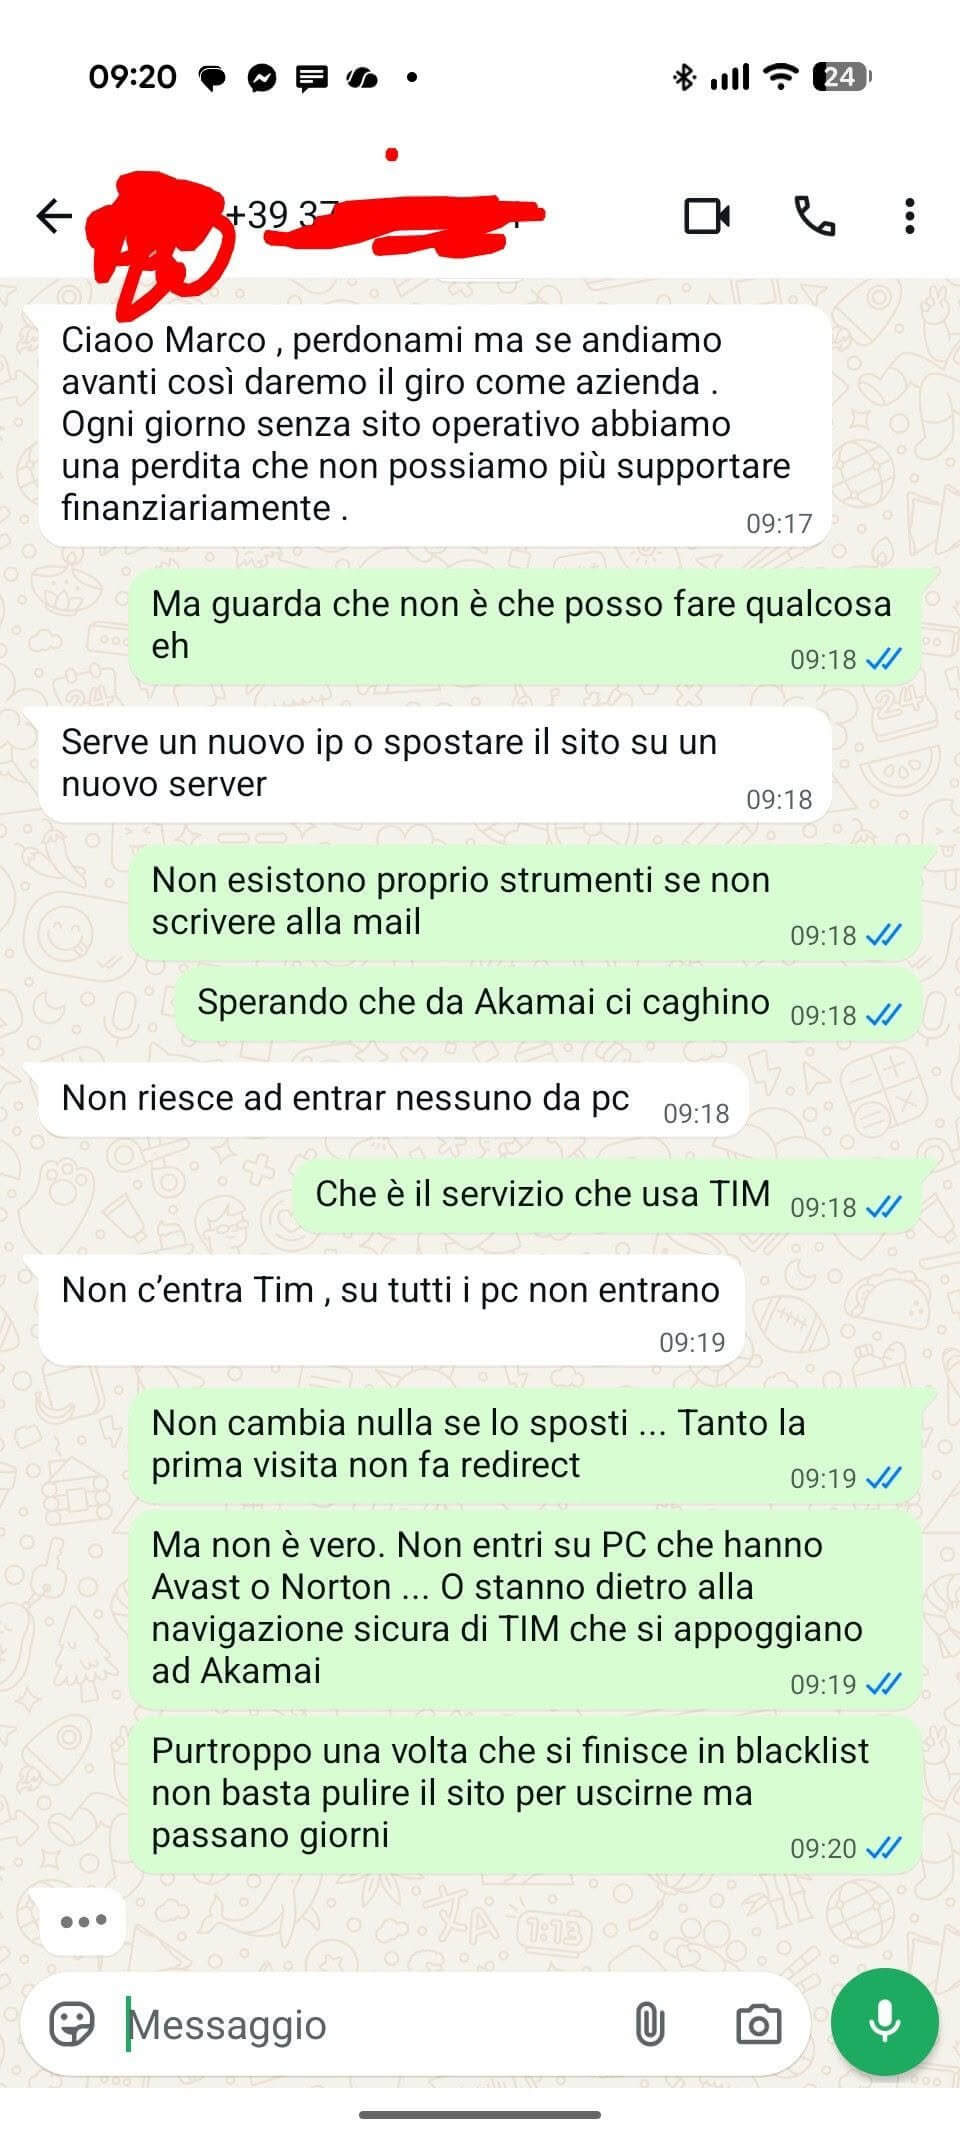
Yet reports are starting to arrive:
«The site doesn't open for me.»
Or:
"I can log in from my cell phone, but not from my computer."
Or again:
«We can't access some of the company's PCs at all.»
It is at this point that a fundamental distinction must be understood.
A technically functioning website is not necessarily a website accessible to everyone.
In fact, there is another level, completely independent from the infrastructure that hosts WordPress: that of domain reputation.
During the time the site was compromised, multiple security systems may have visited, analyzed, and classified it as dangerous.
Once this information is acquired by an antivirus or threat intelligence platform, subsequent removal of the malware from the server does not necessarily result in immediate deletion from the blacklist.
And this is where the problems begin.
TIM Safe Browsing, TIM Guardian, and blocking before even reaching the server
One of the most difficult cases to manage in Italy concerns TIM Safe Navigation.
The principle is relatively simple.
When a TIM user uses the secure browsing service, the request may be subjected to reputational checks before actually reaching the site.
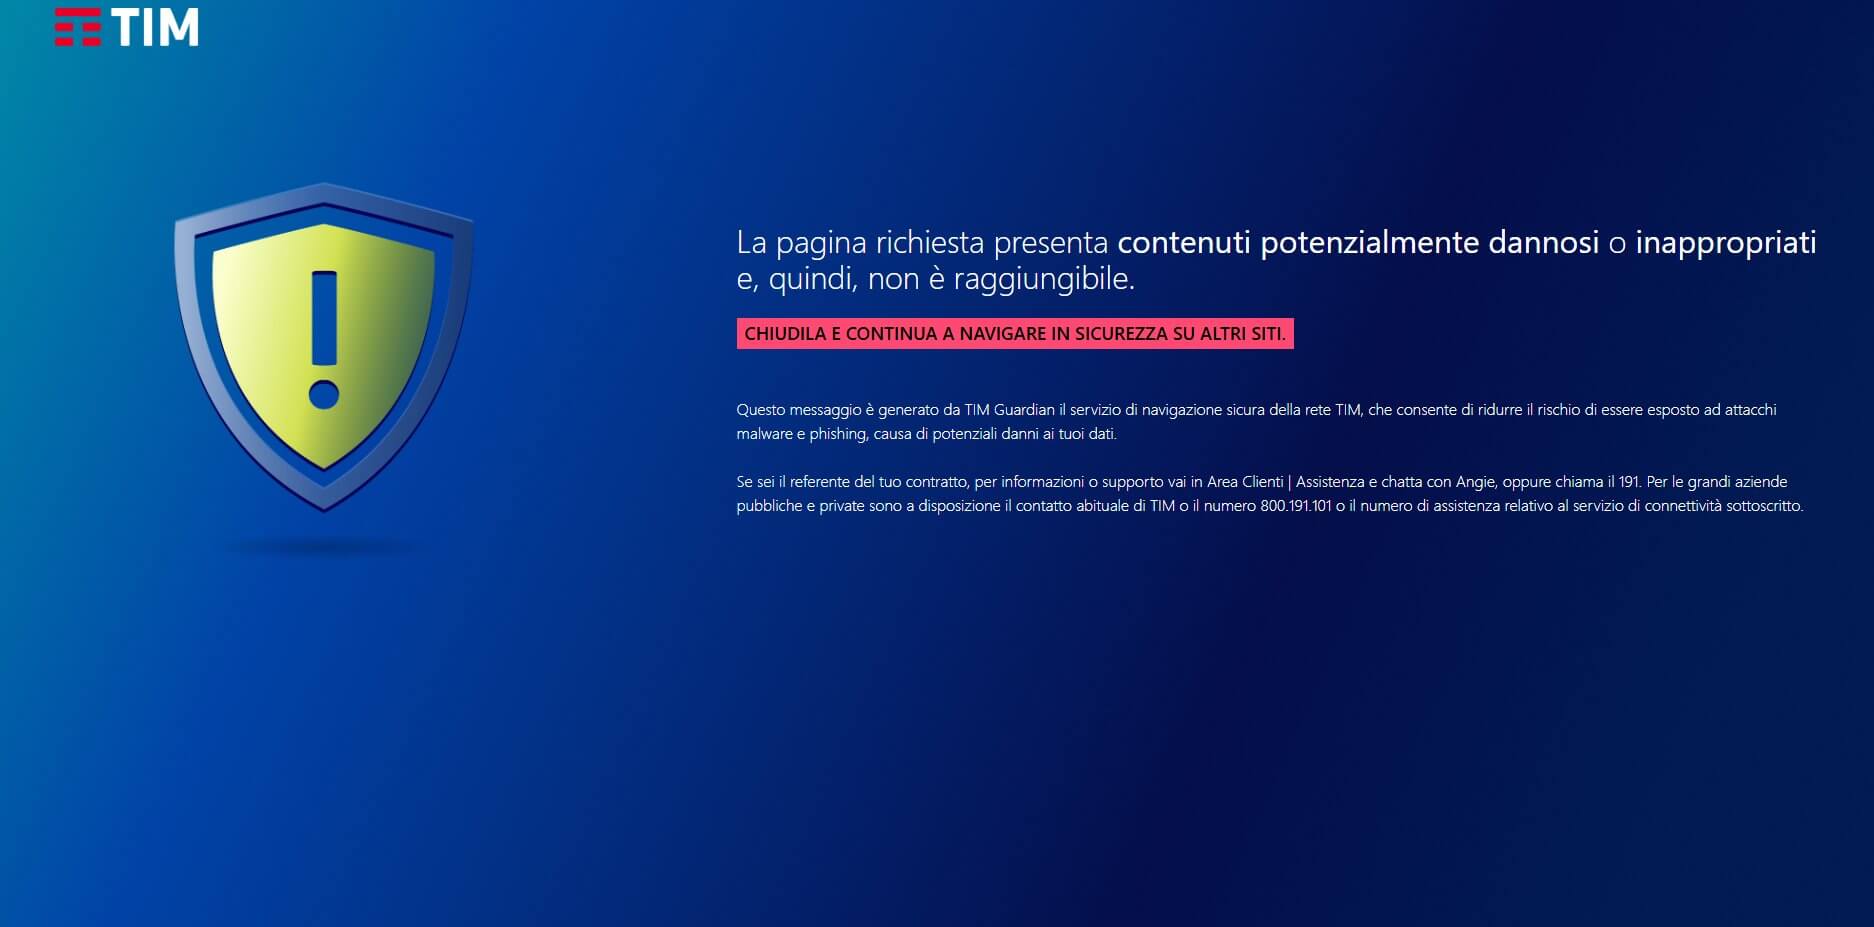
The flow, simplifying, can be represented as follows:
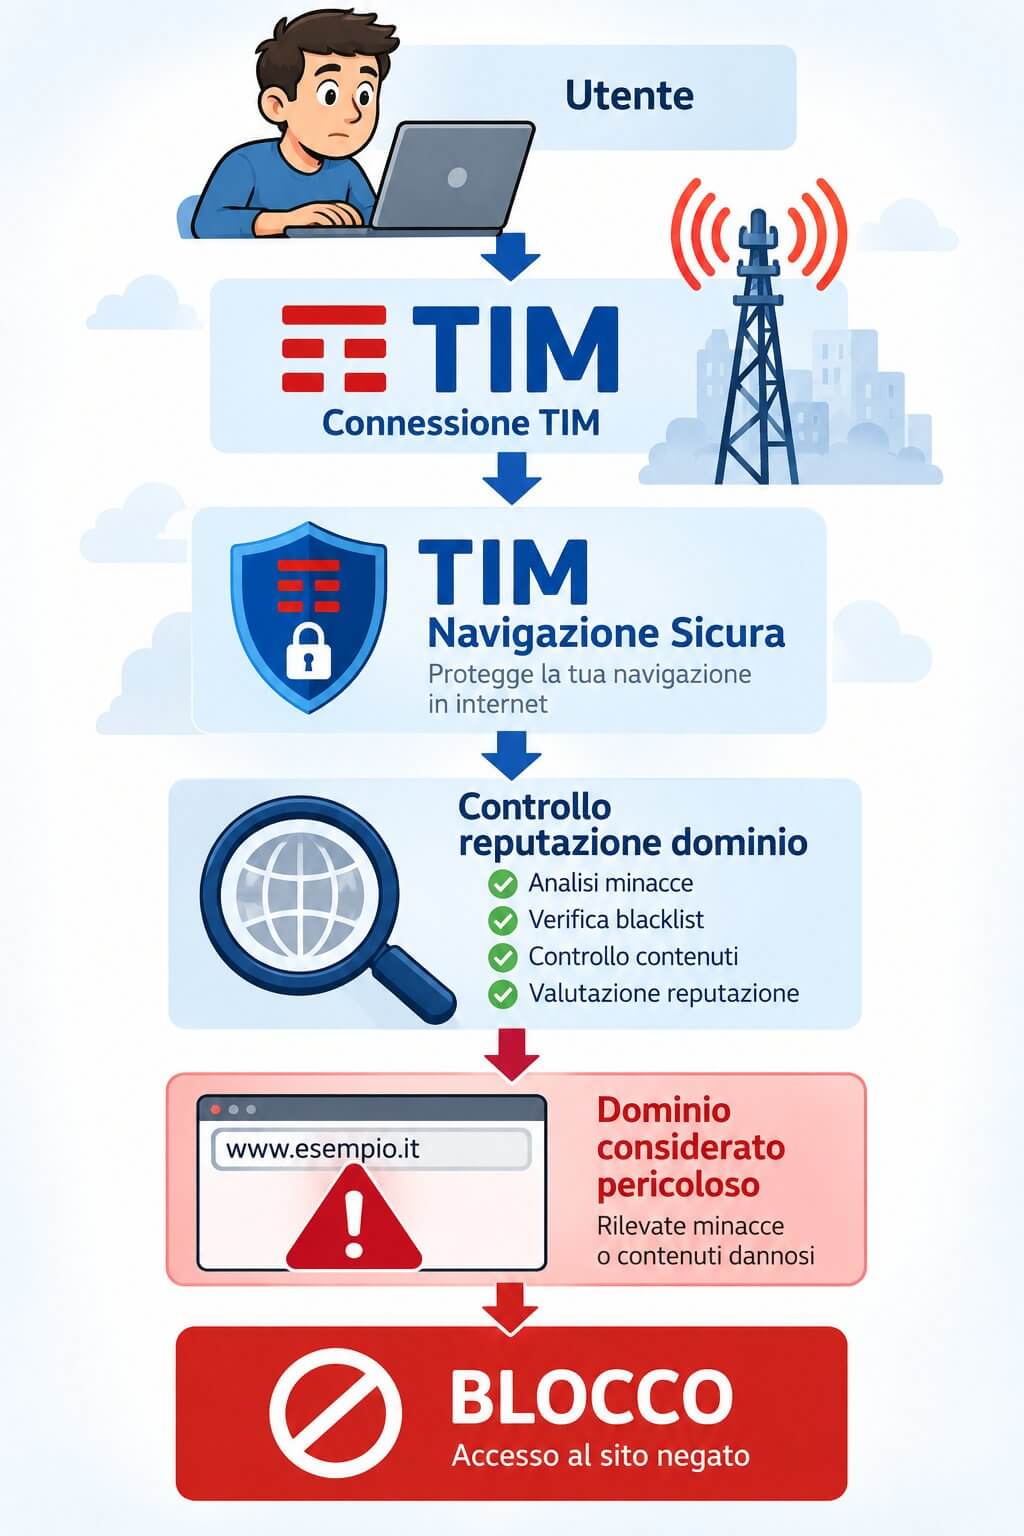
The important detail is precisely this:
The web server may not be reachable at all.
From a systems perspective, we can have a perfectly functioning machine, NGINX correctly configured, PHP-FPM operational, database available and WooCommerce responding in a few milliseconds.
Nothing changes.
If the blocking occurs first, either on the user's network or within the secure browsing system, there is no NGINX configuration that can fix the problem.
It's not a 500 error.
This is not a PHP timeout.
It's not Varnish.
It's not MySQL.
It's not a CPU or RAM issue.
It's a reputation problem.
"We change IP or move the site to another server"
When the problem becomes economically urgent, one of the first solutions proposed is almost inevitably:
«Let's move everything to a new server.»
Or:
"Let's change our IP address."
Understandable.
But in most cases you first need to understand what has actually been blacklisted.
If the problem is with IP address reputation, changing your IP address might actually make sense.
If, however, the domain is classified as malicious, the situation changes completely.
Let's assume that:
www.example.it
be classified as a dangerous site.
Move it from:
192.0.2.10
a:
198.51.100.20
It doesn't change the fact that the user is still trying to reach:
www.example.it
The blacklist still sees the same domain.
The result therefore risks being an emergency migration, with all that this entails, without having actually eliminated the cause of the blockage.
Cleaning up your site and restoring your reputation are two different jobs.
This is probably the most important aspect to understand when handling such an incident.
There are at least two completely distinct phases.
The first is technical remediation.
It means to check:
- modified WordPress files;
- compromised core;
- vulnerable plugins;
- compromised themes;
- webshell;
- backdoor;
- obfuscated PHP code;
- JavaScript injected;
- malicious redirects;
- abusively created administrator users;
- suspicious crons;
- database changes;
- potentially compromised FTP, SSH, or WordPress credentials.
After that, the vulnerability that allowed entry must be resolved.
Because removing the malware without closing the vulnerability simply means waiting for the next compromise.
The second phase is completely different:
restore domain reputation.
During the period of the attack, the site may have been observed by Google, antivirus software, automated crawlers, anti-phishing services, commercial blacklists, DNS security providers, and threat intelligence platforms.
These systems have their own memory.
The compromise may have been resolved as of 10:00 AM today.
This doesn't mean that everyone has already changed their classification by 10:01.
Avast, Norton, and other antivirus programs: the problem is getting bigger.
In the specific case we handled, the situation did not only concern TIM.
The domain was also intercepted by extremely popular antivirus programs such as Avast and Norton , as well as other reputation systems.
At that point the problem becomes even more serious.
Because the user can be blocked for completely different reasons.
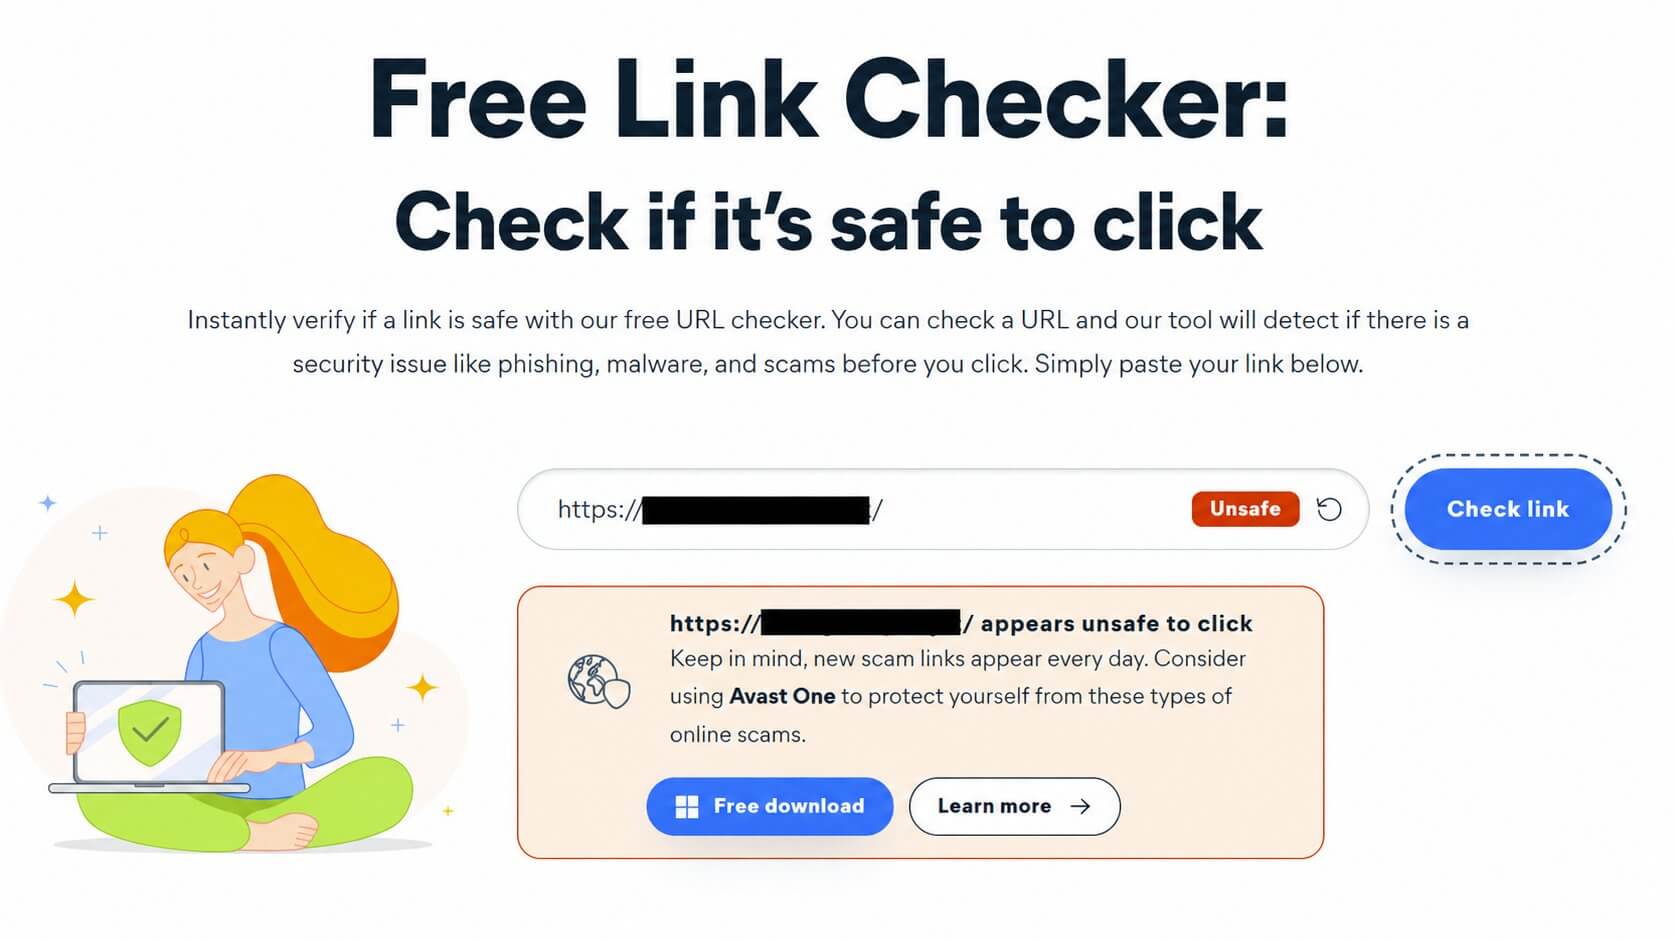
It can be connected via TIM Safe Navigation.
You may have Avast installed on your PC.
You can use Norton.
You may have a corporate Web Security product.
It can browse through filtered DNS.
It may be behind a corporate firewall that imports third-party reputation feeds.
For the end user, the result is still identical:
the site does not open.
And above all, the average user makes no distinction between a block caused by an antivirus and a truly offline server.
The conclusion will be simply:
«The site is not working.»
For a WooCommerce every hour has a cost
This would already be a serious problem for any site.
For an e-commerce it becomes decidedly worse.
In our case, we are talking about an online clothing store created with WooCommerce , therefore a site whose operation directly generates revenue.
We're not just talking about losing a few blog visits.
Any user who cannot reach the site is potentially:
- a product not displayed;
- an unstarted cart;
- an incomplete cart;
- a wasted advertising campaign;
- a lost sale;
- a customer who will likely purchase from a competitor.
Based on the normal volume of business at the store, the damage resulting from a day of severely compromised operations can be estimated at approximately 4.000 euros per day.
And this makes clear the difference between a security incident and the real cost of a security incident.
Let's just imagine that the problem persists for a week.
We're potentially talking about tens of thousands of euros in turnover at risk.
And the server, paradoxically, could be perfectly online all the time.
Losing 30% of your traffic immediately is not an absurd hypothesis but pure reality
Naturally, we cannot establish a universal percentage that is valid for every site.
It depends on the composition of the traffic, the operators used by customers, and the devices and security software installed.
But when a domain is simultaneously blocked by a major Italian operator and by widely used antivirus programs such as Avast and Norton, it is not at all unrealistic to assume an immediate loss of at least 30% of traffic.
In certain audiences it may even be higher.
Let us also consider another aspect.
Lost traffic is not necessarily recovered.
If a customer is looking for a jacket, a pair of shoes or another item of clothing and receives a warning from their browser or antivirus like:
DANGEROUS SITE
he will hardly think:
«I'll try again tomorrow.»
Much more likely, he will return to Google and open the next result.
Maybe that of a competitor.
Reputational damage to the user
There is also damage that is even more difficult to measure.
Trust.
For an e-commerce site, perceived security is fundamental.
The user must enter:
- Name;
- surname;
- address;
- email;
- telephone number;
- order information;
- possibly data related to the payment.
If just seconds before, their antivirus software warned them that the site might be dangerous, convincing them to buy later can become extremely difficult.
Even after the delisting.
This means that the damage from a compromised site doesn't necessarily end when the infected files are removed.
It can continue through the technical reputation of the domain and even into human perception of the brand.
The problem with blacklists: everyone has their own timeframe
One of the most frustrating aspects is that there is no single central Internet blacklist.
Each vendor has its own systems.
Google may consider the site clean.
Avast can continue to report it.
Norton may have a different classification.
TIM Safe Navigation can continue to block it.
Another service may have already removed it.
Yet another may never have entered it.
It is therefore perfectly possible to find yourself in this situation:
Google Safe Browsing CLEAN Antivirus A CLEAN Antivirus B MALICIOUS TIM Safe Browsing BLOCKED Other service CLEAN
And that's precisely why the post-compromise phase must include reputational monitoring , not just server verification.
With TIM, delisting is not particularly simple
Here we come to probably the most unpleasant part of the whole story.
Some services offer relatively simple procedures for requesting domain revaluation.
TIM Safe Navigation uses Akamai technologies for its security infrastructure.
Akamai provides specific tools to challenge a domain's classification and flag it as Non-Malicious Domain , but these tools are primarily part of the professional Secure Internet Access platform.
We therefore do not necessarily have the classic public form available:
Enter domain ↓ Request new scan ↓ Wait for the result
The procedure may require contacting TIM, technical reports, escalation requests to security systems, and, where possible, interventions on the Akamai classification.
This is exactly the kind of situation that is very easy to get into and much more difficult to get out of.
And in the meantime the customer loses 4.000 euros a day
This is the part that is often overlooked when talking about WordPress updates.
An update is being postponed because:
«The site works anyway.»
Or:
«We'll do it next week.»
Or again:
"We don't update because something might break."
Then a vulnerability is published.
The automatic scanners are starting.
The site is identified.
It is being exploited.
The malware stays online long enough to be detected.
And suddenly what seemed like a simple, postponable update becomes a problem capable of producing thousands of euros in damages every day.
We are not saying that every unupdated plugin will automatically lead to a compromise.
We are saying something much simpler:
The longer a known vulnerability remains exposed, the more likely it is that someone will find and exploit it.
And today, finding vulnerable sites on the Internet doesn't necessarily require someone sitting in front of a terminal manually attacking one domain at a time.
Most of the activity is automated.
WordPress security is not about installing a security plugin
Keeping a WooCommerce secure means first and foremost having a procedure.
You need to know:
- WordPress version;
- plugin versions;
- theme versions;
- known vulnerabilities;
- abandoned components;
- administrative users;
- access logs;
- unexpected file changes;
- truly restorable backups.
And most importantly, updates need to be managed , not simply ignored.
Managing also means checking compatibility, making backups, testing the update if necessary, and checking the site afterwards.
On a major e-commerce site, it's perfectly understandable not to want to blindly update during production.
However, it is not a good strategy to transform this caution into months of inaction.
The true cost of prevention is only seen after an accident
Updating WordPress takes time.
Testing a plugin takes time.
Having staging and backups requires resources.
Monitoring vulnerabilities comes at a cost.
Carrying out periodic checks has a cost.
But let's compare it with:
4.000 euros of turnover potentially compromised every day.
With a week of reputational problems.
With Google Ads or Meta campaigns that perhaps continue to drive users to a blocked domain.
With sales staff receiving phone calls.
With customers seeing the malware warning.
With the Webmaster trying to understand why the site works on one connection and not on the other.
With system administrators checking fully functional servers.
With delisting requests to be sent to multiple vendors at the same time.
Suddenly the cost of preventative maintenance looks dramatically different.
The lesson is simple: after a hack, it is not enough to just look at the server.
When a site is compromised, the question shouldn't just be:
"Have we eliminated the malware?"
We should also ask ourselves:
“Who saw that malware while it was online?”
Because Google might have seen it.
TIM might have seen it.
Akamai may have classified it.
Avast may have registered it.
Norton may have entered it into their databases.
And each of these subjects could have different times to notice that the site is clean again.
Conclusions
The incident we described represents one of the lesser-known aspects of WordPress security.
Getting hacked doesn't just mean having to clean up WordPress.
When the compromise lasts long enough to be detected by Internet-wide security systems, the problem can continue long after remediation.
And it's especially painful when the affected site is a WooCommerce that sells online and generates several thousand euros a day.
In this case, even after technically restoring the site, we had to deal with blocks from services like TIM Navigazione Sicura and popular antivirus programs like Avast and Norton.
Moving the site to a new server wouldn't necessarily have solved the problem.
Changing the IP address would not automatically restore the domain's reputation.
Because server reputation and domain reputation are two different things.
And above all, because the Internet doesn't forget a compromise the same moment we delete the last infected file.
It may take days.
In some cases, the after-effects can last for weeks.
Meanwhile, a significant percentage of users may not be able to reach the site and, for an e-commerce site, every lost visit can directly translate into lost revenue.
The moral, then, is not simply:
make backups.
It's something broader:
Keep your WordPress, WooCommerce, plugins, and themes constantly monitored and updated.
Because updating a vulnerability in a timely manner can take half an hour.
Recovering a domain's reputation after a compromise can take weeks.
And when the site generates thousands of euros a day, those weeks can become extremely expensive.

