

Since the General Data Protection Regulation (GDPR) came into force, media attention has focused primarily on the multimillion-dollar fines imposed on tech giants like Google and Facebook, with news and press releases. No one has ever said a word about the Mario Rossi of the moment , who in reality doesn't exist in the collective imagination, because ultimately, only large corporations receive fines, not small businesses.
The decision to exclusively mention the sanctioning activities against these large corporations is mainly due to editorial choices and effective headlines capable of involving public opinion and interest, as well as finding paying clicks.
To stay on the subject, yesterday's news in which Facebook was fined for 1,2 billion euros is still fresh.
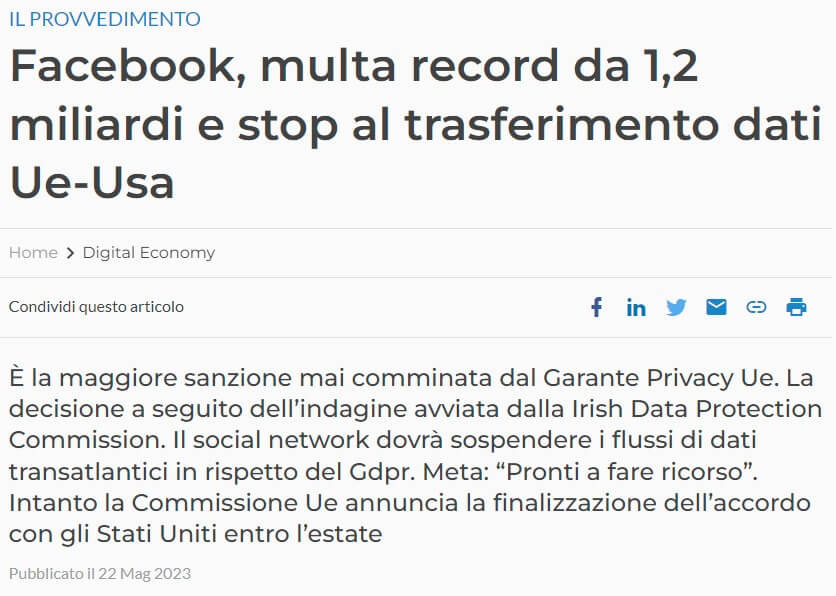
The Irish Data Protection Commission (DPA), acting on behalf of the EU Data Protection Supervisor (EDPB ), has fined Meta €1,2 billion for violating European data protection rules (GDPR) with its social network Facebook . The fine is the highest imposed by a data protection regulator in Europe.
Meta, which intends to appeal, was fined for "continuing to transfer personal data" of users from the European Economic Area to the United States in violation of European regulations.
Meta must also “suspend any transfer of personal data to the United States within five months” of being notified of the decision and must comply with the GDPR within six months.
This focus has created a false belief: the feeling, among many, is that privacy authorities, including the Italian Data Protection Authority, are primarily interested in sanctioning these massive corporations.
In fact, this couldn't be further from the truth.
The GDPR is a European regulation that aims to strengthen and unify data protection for all people within the European Union (EU). It replaces the 1995 data protection directive and introduces strict rules on data protection and data processing. It also provides for heavy penalties for violations, regardless of the size of the entity committing them.
But let's get back to our focus. In an era where Software as a Service (SaaS) and Platform as a Service (PaaS) solutions are increasingly popular, many small and medium-sized businesses, freelancers and even individuals use services that are not GDPR compliant.
For example, image optimization plugins relying on Content Delivery Networks (CDN) of companies based in the United States, without European branches, or hosting services based in San Francisco.
This is because many people mistakenly assume that fines for violating the GDPR only apply to large companies. Yet the truth is that these sanctions affect everyone, without exception.
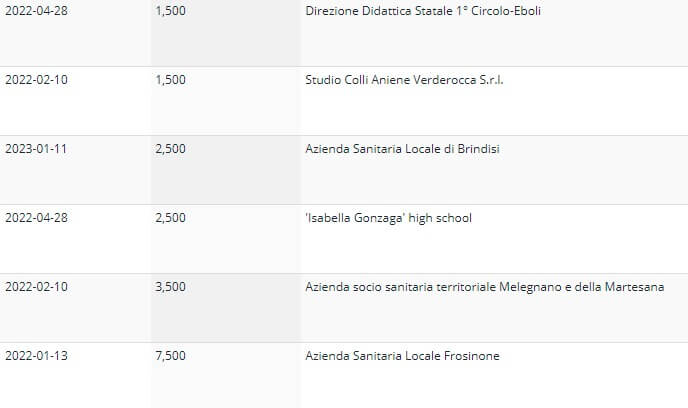
At this point, it's appropriate to clarify and provide tangible proof of the above: there's a website called Enforcement Tracker that provides an overview of the fines and penalties imposed by EU data protection authorities under the GDPR. The goal is to keep the list as up-to-date as possible, although not all fines are made public; therefore, the list can never be complete.

Browsing the site and applying the filter to Italy, we see that 1844 fines have been registered against entities of all sizes: joint-stock companies, limited liability companies, freelancers, and even individuals. The fines vary in amount, with many amounting to around €1000. This clearly indicates that, when necessary, fines are applied to everyone, without distinction.
So, with this awareness, hopefully we can have a more realistic view of the problem than the one conveyed and implied by the media. It is essential to weigh each implementation decision, considering compliance with the GDPR as an indispensable requirement and not as a detail reserved only for the giants of the technology sector.
Remember, GDPR is serious business and penalties affect everyone. None excluded and even if you want to risk a violation of the same you must be well aware that the problem concerns you too.

