

Table of contents of the article:
Cybersecurity is a topic of growing importance in today's world, especially with the emergence of increasingly advanced technologies such as quantum computing. Traditional cryptographic systems, which have dominated the field of digital security for decades, are about to face an existential challenge. Algorithms such as RSA and elliptic curve cryptography, which have protected billions of transactions and communications, risk becoming vulnerable to new types of attacks. However, in the heart of this looming storm, Italian research is making extraordinary progress, with new cryptographic solutions that could define the future of digital security: LEDACRYPT, CROSS and LESS.
The current context of cryptography
Over the past few decades, computer security has relied on cryptographic methods that use public and private keys. The Rivest–Shamir–Adleman (RSA) algorithm and elliptic curve cryptography (ECC) have been pillars of this protection, providing robust mechanisms for encrypting data and ensuring authenticity in communications. RSA relies on the difficulty of factoring large prime numbers, while ECC uses the mathematical properties of elliptic curves to create cryptographic keys that are smaller but just as secure as RSA.
However, with the emergence of quantum computing, it has been realized that these solutions may no longer be sufficiently secure. The reason? Shor's algorithm.
Shor's Algorithm and Quantum Attack
Quantum computing represents a new paradigm in computation, exploiting the properties of quantum physics to solve complex problems much faster than conventional computers. One of the most famous algorithms in cryptography is Shor's algorithm , developed by Peter Shor in 1994.
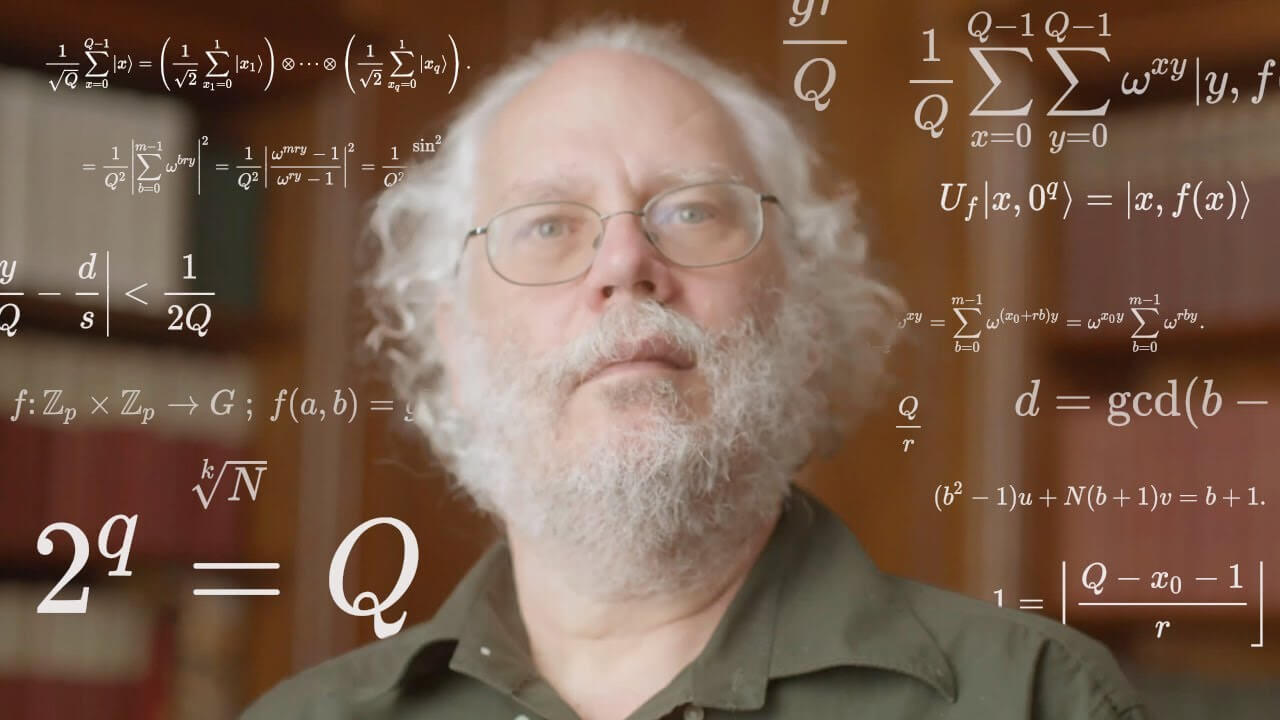
Shor's algorithm is capable of solving two fundamental cryptographic problems: integer factorization and the discrete logarithm problem, which are the foundation of the security of RSA algorithms and elliptic curve cryptography. In a world dominated by classical computing, factoring a 2048-bit number would take billions of years. However, a sufficiently powerful quantum computer could solve it in dramatically less time , undermining the fundamental security of RSA and ECC.
A quantum attack exploits this weakness. Since RSA and ECC rely on the computational difficulty of these problems, a quantum attack, made possible by a quantum computer, would make these algorithms vulnerable. This scenario has given rise to a global race to develop new cryptographic systems resistant to quantum computers: and this is where LEDACRYPT, CROSS and LESS, the three algorithms born from Italian research, come into play.
The Role of Italian Research in Post-Quantum Cryptography
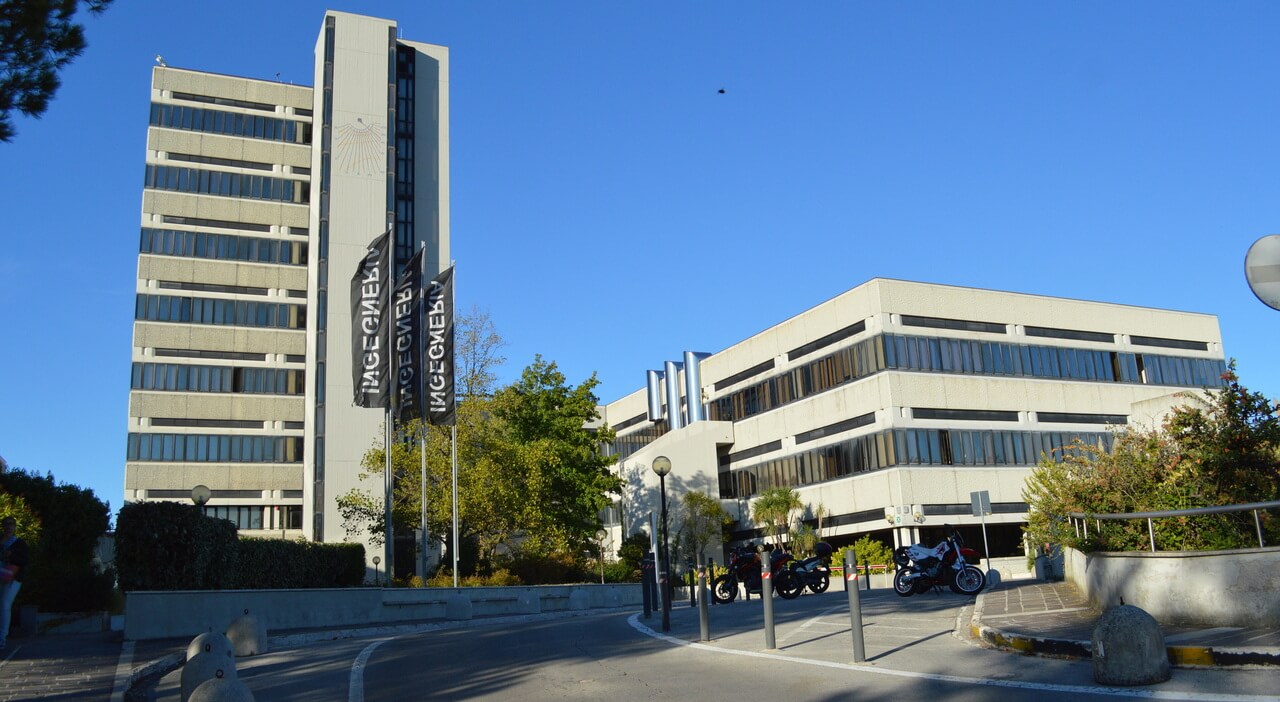
The Polytechnic University of Marche (UNIVPM) is one of the Italian institutions that has taken a leading role in the development of new cryptographic solutions suitable for the quantum era. In collaboration with the American National Institute of Standards and Technology (NIST), the Polytechnic University of Marche has developed and refined cryptographic algorithms aimed at solving the problems posed by future quantum attacks. Among these, LEDACRYPT , CROSS , and LESS stand out.
LEDACRYPT: Long-term protection against quantum attacks
LEDACRYPT is an algorithm based on error-correcting codes, specifically designed to be resistant to quantum computers. Error-correcting codes are used to correct errors in data transmissions, but their application in cryptography is relatively recent. LEDACRYPT uses these codes to create complex cryptographic keys that remain secure even in the face of attacks by quantum computers.
The algorithm is based on a variant of LDPC (Low-Density Parity-Check) ciphers, also used in satellite communications and high-efficiency telecommunications systems. The robustness of these ciphers, combined with advanced cryptographic techniques, makes LEDACRYPT one of the most promising solutions for post-quantum cryptography.
CROSS: A Post-Quantum Public Key System
Another significant Italian contribution is CROSS , a cryptographic algorithm that aims to replace traditional public-key systems like RSA and ECC. CROSS uses a completely different approach, relying on mathematical problems that, according to current research, remain difficult to solve even with the aid of quantum computing.
CROSS uses a combination of techniques based on lattice theory, a field of mathematics that is currently considered one of the most promising foundations for post-quantum cryptography. Lattice-related problems, such as the shortest vector approximation problem (SVP), are much more complex than prime factorization or discrete logarithm solving, making CROSS resistant to quantum attacks.
LESS: Security for Low Resource Devices
While LEDACRYPT and CROSS aim to ensure data security in computationally intensive environments, LESS is specifically designed for resource-constrained devices, such as IoT (Internet of Things) sensors, mobile devices, and other low-power systems. LESS (Lightweight Encryption for Securing Systems) uses lightweight cryptographic techniques that provide quantum security without requiring significant computational resources, making it ideal for devices that cannot support more complex algorithms like LEDACRYPT or CROSS.
LESS is based on a combination of symmetric encryption and data compression techniques, which allows it to offer robust security while maintaining minimal usage of system resources.
The challenge of quantum computers
Quantum computing has the potential to revolutionize many fields, from chemistry to medicine, but it also poses a significant threat to cybersecurity. Quantum computers are capable of performing parallel calculations exponentially faster than classical computers, which is what makes current cryptographic algorithms like RSA and ECC vulnerable.
Shor's algorithm, for example, is designed to exploit the parallel processing power of quantum computers to factor large numbers into prime factors in dramatically reduced times. This makes RSA, which relies on the difficulty of factoring prime numbers, highly vulnerable. Elliptic curve cryptography, while based on a different mathematical problem (discrete logarithm on elliptic curves), is subject to a similar vulnerability.
The fundamental problem is that many of the cryptographic algorithms currently in use are not designed to be resistant to quantum computers. While these computers are not yet powerful enough to perform large-scale attacks, their development is progressing rapidly. Estimates vary, but many experts believe that a quantum computer powerful enough to run Shor's algorithm at scale could be developed in the next 10 to 20 years.
The Future of Cryptography: Towards a Post-Quantum World
In response to this emerging threat, the scientific and industrial community is actively working to develop cryptographic algorithms that can withstand quantum attacks. NIST , in particular, has initiated a standardization process for post-quantum cryptography, with the goal of identifying and certifying algorithms that can protect data even in the era of quantum computers.
LEDACRYPT, CROSS, and LESS represent Italy's contribution to this global challenge. These algorithms not only aim to protect critical data from future quantum attacks, but also demonstrate how research and innovation can thrive in leading Italian academic and scientific environments.
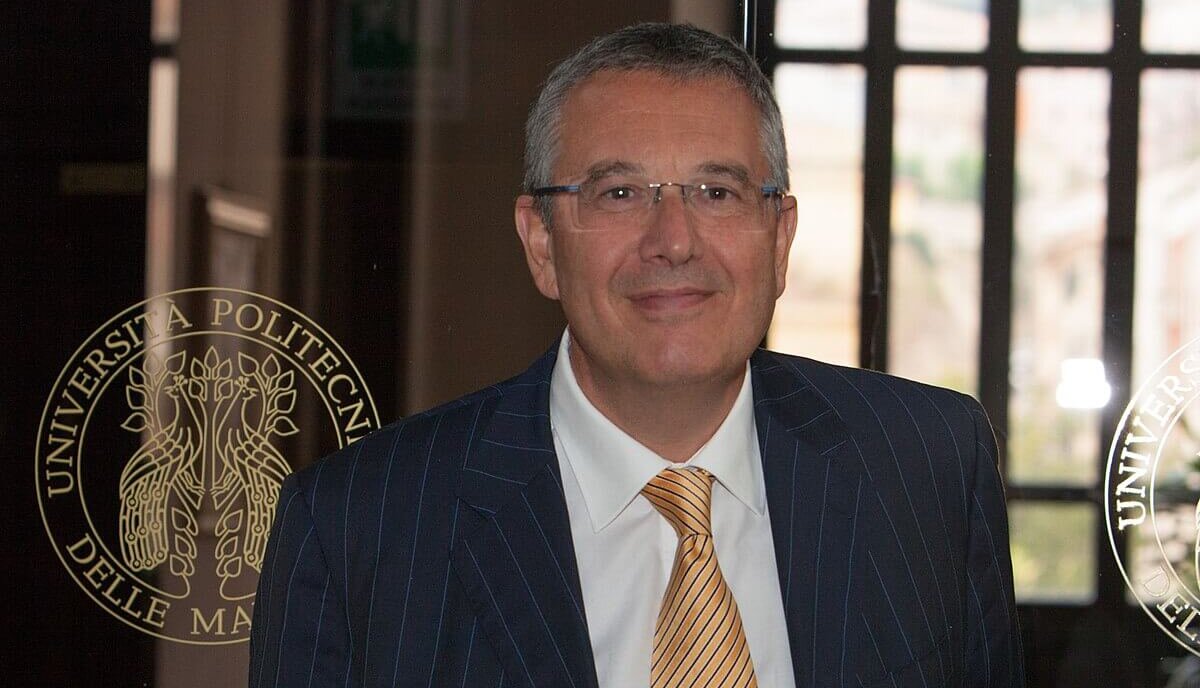
"This achievement was possible thanks to the talent and hard work of the telecommunications research team," says Rector Gian Luca Gregori , "who have achieved and maintained the highest standards of international scientific research in this field, as evidenced by numerous high-profile international publications."
However, widespread adoption of post-quantum solutions will take time. Many critical systems currently using RSA and ECC will need to be migrated to more secure algorithms, and this will require a coordinated effort between governments, industries, and academic institutions. However, with the development of new technologies such as LEDACRYPT, CROSS, and LESS, we can be optimistic about humanity’s ability to address future challenges.
Conclusion
Cryptography is about to undergo one of its most significant changes since the invention of modern public key systems. With the emergence of quantum computers, RSA and elliptic curve cryptography could become obsolete in the not too distant future. However, Italian research is proving to be at the forefront of the development of post-quantum cryptographic solutions. LEDACRYPT, CROSS and LESS are three algorithms that not only address the challenges posed by quantum computing, but also represent the potential of Italian innovation in the field of cybersecurity. Thanks to these new technologies, the future of cryptography could be not only more secure, but also more efficient and suited to the needs of the ever-evolving digital world.

