

Table of contents of the article:
Over the past ten years, our previous email server has played a crucial role in managing corporate communications, proving to be a reliable and high-performance tool. However, with technological evolution and the increasing need for security and flexibility, we felt it necessary to undertake a process of upgrade and innovation. It is with great excitement that we announce, starting today, March 1st, the transition to our new multi-user email system solution, based entirely on a proprietary cloud platform.
This decision is the result of a careful assessment of company needs, combined with the desire to offer our customers an increasingly reliable, safe and cutting-edge service. The implementation of the new mail system represents an important step forward in our strategy of digitalization and optimization of company resources.
In this article, we'd like to share with you, our readers and customers, the journey that led us to the development and launch of our new email solution . Together, we'll explore the implementation process, highlighting the new system's key features and benefits, the software we chose to run it, and the rationale behind our technological and technical-strategic choices. The goal is to provide an in-depth look at the innovations we've introduced and how they translate into added value for our customers and the efficiency of their daily operations.
The transition to our proprietary Cloud solution marks a significant moment in our company history, reflecting our ongoing commitment to excellence and customer satisfaction. With this move, we place ourselves at the forefront of the technological landscape, adopting the most modern infrastructures and software solutions to guarantee superior performance, greater scalability and uncompromising security.
We invite you to follow us in this detailed exploration of our new email system, convinced that it represents not only a qualitative leap for our company, but also a model of innovation and best practice for the entire sector.
The need for a new Mail Server
The decision to migrate to a new solution for our email system was not made lightly, but was the result of a careful assessment of the needs and technical challenges encountered with our previous mail server. The existing system, based on a proprietary solution developed on CentOS 6, reached the end of its useful life, entering the End of Life (EOL) phase in November 2020. This meant CentOS 6 stopped receiving official security and system updates, potentially exposing our infrastructure to vulnerabilities that could not be mitigated through new patch releases. While we were using unofficial repositories and specific, non-vulnerable kernel versions, it was equally true that the time had come to say goodbye to a system that had served its purpose admirably but was nevertheless beginning to show the first signs of operational failure.
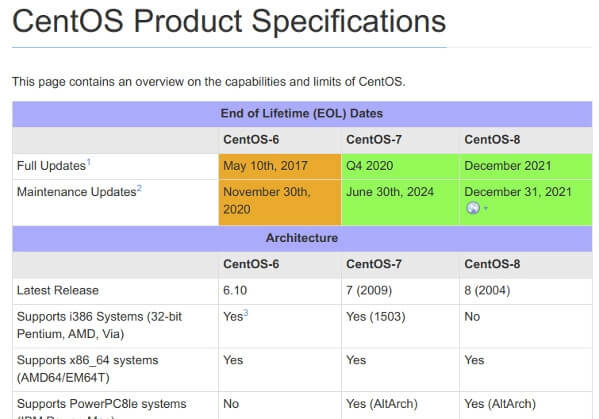
Management and maintenance of the old system had become increasingly complex and sensitive, partly due to the need to use unofficial Linux kernels from ELRepo repositories to keep defenses against security threats up to date. While these kernels could offer some level of up-to-date security, many software components critical to the operation of the mail server were no longer up to date. This technological deficit translated into significant limitations in terms of performance, stability and availability of new features, essential to effectively respond to constantly evolving business needs.
While email is not our company's core business, managing over 25.000 active email accounts requires rigorous monitoring of the service's stability, efficiency, and functionality . This requirement was further highlighted in early February, when we first encountered a very specific bug that affected a single customer but compromised the stability of the entire IMAP server. The bug was attributed to an outdated version of Dovecot, highlighting the inherent and unexpected problems of outdated software.
The urgent need to update a single component like Dovecot has therefore accelerated our decision to bring forward the transition to the new mail server, originally scheduled for June 2024. The new solution, based on cutting-edge technologies and Cloud infrastructures, not only solves the issues related to security and technological obsolescence but also offers significant improvements in terms of performance, scalability and feature innovation. This change of direction was driven by the knowledge that a modern, efficient and secure email system is essential to supporting business activities and ensuring the best possible experience for our customers.
Commercial or Open Source Mail Servers created ad hoc?
In the evaluation process for revamping our email system, we were faced with a crucial decision: opt for a commercial solution or develop a custom Open Source solution. Initially, the idea of adopting a commercial solution seemed appealing. This option promised to free us from the burdensome tasks of implementing, managing, and updating the system, giving us the ability to focus on other aspects of our business. Paying for a license and relying on a "turnkey" product might have seemed the simplest and most direct route.
However, our analysis of the various commercial solutions available on the market raised several concerns. We discovered that, in many cases, the proposed pricing models were not compatible with the cost structure of our services. In practical terms, this meant we would end up spending more on licenses than we could generate from selling the service itself . Some pricing models were based on the number of mailboxes rather than the number of mail servers, making the costs unacceptably high for our business model. Furthermore, we found that some companies offered solutions based on open source and public domain software already known to us, charging a premium for their custom interfaces.
Another major concern was our reliance on third-party vendors for maintenance and technical support. Considering that in our more than 10 years of operation, we'd experienced a maximum of half an hour of downtime, the idea of having to wait for an external support team to resolve any issues was unthinkable. The prospect of relying entirely on a third-party technology solution posed significant risks, including changes in licensing models, price increases, or worse, the vendor's going out of business.
Furthermore, the idea of engaging in a sort of "marriage" with all these unknowns, doubts and perplexities, together with the annual license cost which varied between 5000 and 10.000 euros (translating into an investment of at least 50.000 euros over a period of 10 years), led us to seriously reconsider our strategy.
Already having the experience and expertise necessary to develop an in-house solution, as we did with our previous mail server, we decided to pursue this path . This approach allowed us to add new features and functionality, while also improving aspects of the previous system that were limited by the restrictions of outdated software. The decision to develop a custom open source solution gave us the freedom to customize the system according to our specific needs, while ensuring complete control over the security, stability, and efficiency of the service. This decision reflects our commitment to providing cutting-edge solutions while maintaining independent and flexible management of our technological infrastructure.
Dedicated server or Cloud?
The decision between maintaining dedicated servers or migrating to a cloud solution for our multi-domain corporate email system was a crucial decision when planning our new mail server. The previous configuration relied on two dedicated, redundant physical machines with a shared file system, a solution that guaranteed high reliability in terms of uptime, even during maintenance or failures, as well as optimal load management for outgoing mail. Despite these advantages, being tied to physical systems and, consequently, the underlying hardware, did not fully meet our expectations for the future.
The goal was to overcome the limitations imposed by physical hardware, aiming for a more flexible and scalable solution . We would have preferred to adopt a clustered architecture, based on dedicated instances, with an elastic and expandable file system capable of easily adapting to our growth needs, scaling from the current 8 terabytes to tens of terabytes easily and quickly, through the allocation of CEPH network volumes.
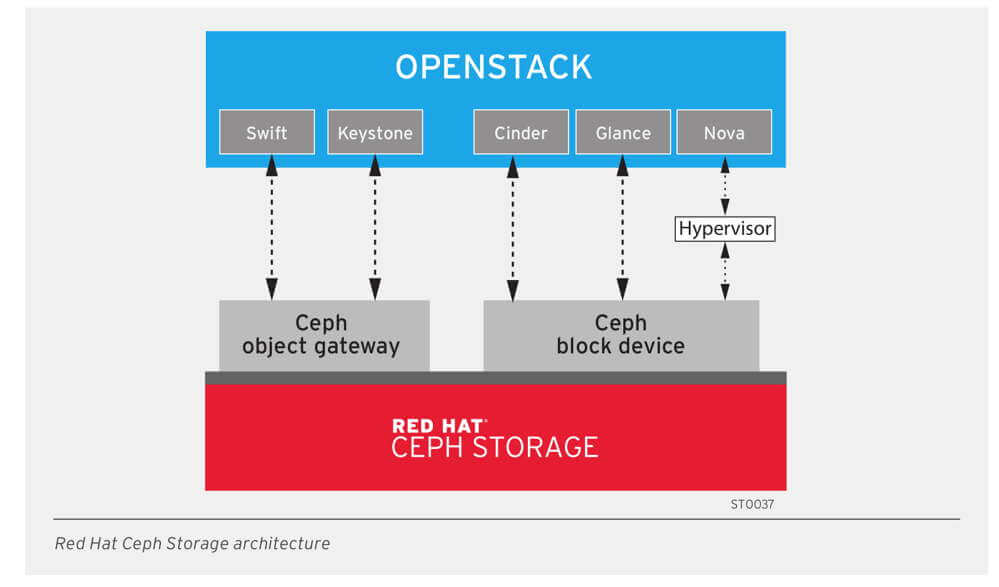
Furthermore, the previous configuration used mechanical SAS drives, which, while reliable, had limitations in terms of performance, latency, and the ability to handle significant concurrent access—say, 5000 users accessing email simultaneously—with read speeds no higher than 200 MB/s. The prospect of switching to CEPH on latest-generation NVMe drives promised an exponential improvement in performance, as confirmed by our preliminary tests, which showed transfer speeds exceeding 1,5 GB/s, marking a 700% performance increase.
This notable acceleration would not only be beneficial during peak load periods, but also during nightly dual geographic SAN backup operations, significantly improving system efficiency and resilience.
Considering these premises and after a careful evaluation of the pros and cons, we made the decision to virtualize the entire infrastructure on the Cloud. The choice to use OpenStack and CEPH network volumes on latest generation NVMe devices proved to be the optimal strategy to guarantee the scalability, flexibility and high performance we were looking for. This transition marks a significant step forward in our ability to effectively and efficiently manage the growing volume of data and demand for services, laying the foundation for a modern, reliable and future-ready email infrastructure.
The need for a turnkey and transparent migration
For us, the primary goal in switching from the old to the new email infrastructure was to ensure a completely seamless and painless transition for users. The challenge was twofold: on the one hand, it was unthinkable to handle support requests from over 10.000 people the day after the switch; on the other, it was crucial not to alter users' workflow in any way . Even the slightest change—be it a change in the color of a button, a logo, or a text—could generate anxiety and confusion among less experienced users, resulting in a wave of helpdesk calls and emails requesting support. This is especially true in an environment like ours, where end users can range from technically competent professionals to secretary-at-large retiring employees.
Our goal was therefore to create a kind of "magic," orchestrating a game of skill where users wouldn't notice anything except a marked improvement in the quality of service. This meant they'd only read about the migration through this article, without noticing any disruption in their daily email usage.
To achieve this, we meticulously planned every step of the migration. We replicated the existing software configuration on the new platform, updating it with the latest versions and replacing those components that had room for improvement. This approach ensured that, from the end user's perspective, nothing changed: the hosts and URLs remained the same, as did the control panels, passwords and every other familiar interface element.
The result was exactly what we hoped for: a migration that was invisible to users, allowing them to continue using their email services without interruption or disruption, unaware of the complex technological work being done behind the scenes. This transparency was key to maintaining our users' trust and peace of mind, demonstrating that significant technological changes can be implemented without negatively impacting the user experience.
Prepare well in advance: the migration strategy
Careful planning was key to a successful transition to the new corporate email system. Aware of the importance of this step, we began preparing well in advance, establishing a preventive time frame of 20 days. This period was dedicated to the allocation of 8 new IP addresses intended to replace those in use on the old mail server. The choice to renew the IP addresses was not random, but motivated by the awareness that, in their past, some of these may have been involved in unwanted activities such as sending SPAM, thus finding themselves included in anti-spam lists or blocked by the main suppliers of email services such as Google, Microsoft, Yahoo, and others.
To mitigate this risk and ensure a smooth transition, we have undertaken a thorough review of the 8 new IP addresses. Using a test domain allocated on the new mail server, we carried out several tests of sending emails to recipients belonging to the most well-known email services, both international and Italian, such as tim.it, alice.it, libero.it, and others. This preliminary test revealed that, on two specific occasions, one IP was rejected by Microsoft and another by Google, while all others were accepted without problems.
A key part of this verification process involved DNSBLs (DNS-based Blackhole Lists), which are public databases used to identify IP addresses known to be sources of SPAM or other types of email abuse. Tools such as DNSBL.info and MultiRBL (Multi-Valley) were used to ensure that our new IP addresses were not present on these blacklists. DNSBL.info and MultiRBL are online services that allow you to check the presence of a given IP address on multiple DNSBLs simultaneously, thus providing a comprehensive picture of an IP's reputation and trustworthiness for sending emails.
Thanks to these preventive measures and scrupulous control, we have achieved a level of satisfaction and reputation of the IP addresses that guarantees a smooth execution of the implementation of the new mail server. This preliminary preparation phase, characterized by careful planning and in-depth technical checks, laid the foundation for an effective migration, minimizing the risks of outages or IP reputation issues in the context of our new email infrastructure.
Choosing software for the new mail server
In the project to renew our mail server, we aimed to maintain continuity with the pre-existing infrastructure, while introducing significant improvements in terms of performance and security. The choice of software played a crucial role in this phase, orienting us towards solutions that could guarantee a smooth transition and at the same time represent a qualitative leap compared to the past.
1. The operating system: AlmaLinux 9
For the heart of our new email system, we have chosen to continue to rely on an operating system derived from RHEL (Red Hat Enterprise Linux), opting for AlmaLinux 9 as the natural successor to the previous CentOS.
The choice was between Rocky Linux and AlmaLinux, as both operating systems are forks of RHEL created in response to Red Hat's decision to move CentOS from a downstream distribution (based on the Red Hat Enterprise Linux (RHEL) source code) to an upstream distribution (CentOS Stream) and prohibit the distribution of the source code to non-subscribers.
While we recognize the value of RockyLinux, a distribution developed and supported entirely by the community, CentOS's history has raised concerns about the long-term sustainability and reliability of exclusively community-driven distributions. This context has prompted us to take a closer look at AlmaLinux. While AlmaLinux enjoys strong support from the GNU/Linux community, it is important to emphasize that it does not position itself exclusively as an "Enterprise Community Driven" distribution. This distinction has allowed us to explore a solution that, while rooted in the values of the open source community, offers a support and development model that is not solely dependent on community volunteerism, but also leverages more robust legal and financial organizational structures.
AlmaLinux is developed and supported by CloudLinux, through its TuxCare division . CloudLinux has a long history of providing security and stability solutions for Linux servers, especially in the hosting space. Their experience is reflected in the development of AlmaLinux, with a strong focus on binary compatibility with RHEL and a long-term commitment to security and support.
AlmaLinux's FIPS certification is crucial for organizations operating in regulated environments or handling sensitive data. FIPS certification validates that the cryptographic modules used in the operating system meet the standards established by the U.S. National Institute of Standards and Technology (NIST) . This is particularly important for industries such as the federal government, healthcare, and finance, where compliance with security standards is mandatory.
We have therefore adopted AlmaLinux finding it important to obtain the following advantages:
- TuxCare support: Benefiting from the support of a company with extensive experience in the field of security and stability of Linux systems, AlmaLinux enjoys timely updates and robust technical support.
- FIPS certification: FIPS certification means that AlmaLinux is suitable for environments that require high levels of security and compliance, making it a solid choice for organizations that need this certification for their operating systems.
- Stability and Reliability: Close compatibility with RHEL ensures that AlmaLinux users can benefit from a stable and reliable operating system, with a wide range of supported and tested software.
AlmaLinux presents itself as an open-source, community-driven Linux distribution, created as a direct alternative to CentOS following Red Hat's decision to move CentOS Stream. With extended support until 2032, AlmaLinux 9 promises stability, security, and a clear roadmap for future updates—essential elements for the operational continuity and resilience of our mail server.
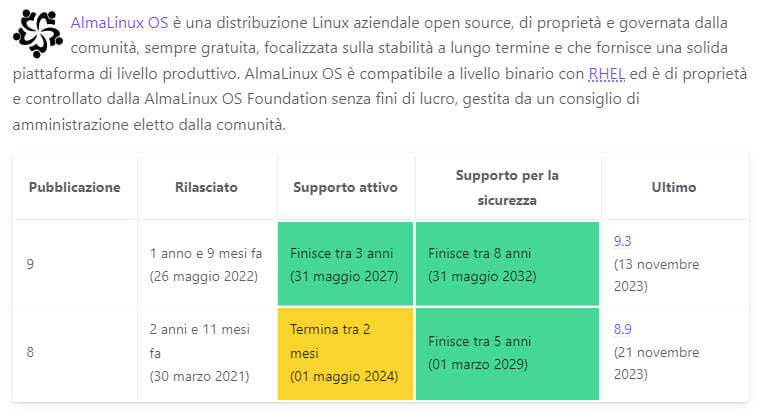
The choice of AlmaLinux was guided by the need to ensure a solid and reliable foundation for our system, with the guarantee of long-term support that allows us to plan the future with greater serenity. Adherence to RHEL standards also guarantees broad compatibility with software and applications, facilitating the integration of new technologies and the management of any problems.
The addition of a cutting-edge repository such as ElRepo allowed us to install the latest Kernels updated to the 6.7 branch and immediately obtain benefits in terms of network stack, memory and process management, as well as the now usual TCP BBR can improve TCP/IP connections even in areas of poor coverage.
2. MTA Server: Postfix
As for the MTA (Mail Transfer Agent) server, we have renewed our confidence in Postfix , confirming it as the preferred choice over alternatives such as Sendmail, Qmail, and EXIM. The decision to continue with Postfix was driven by its reliability, scalability, and relative ease of configuration and management, aspects that make it particularly suited to our needs.
A key factor in choosing Postfix was its compatibility with the MySQL backend , which we use to efficiently manage users, domains, aliases, forwarding rules, and autoresponders through the PostFixAdmin interface . This integration allowed us to seamlessly import and migrate the existing mail user database from the old server, ensuring essential business continuity during the transition phase.
The combination of Postfix and MySQL provides a robust and flexible solution for our email environment, allowing us to optimize resource management and implement advanced security policies. The ability to fine-tune mail routing rules and dynamically manage users through PostFixAdmin has been a significant step forward for us in achieving a more secure, high-performance, and scalable email service.
3. POP3 and IMAP server with Dovecot
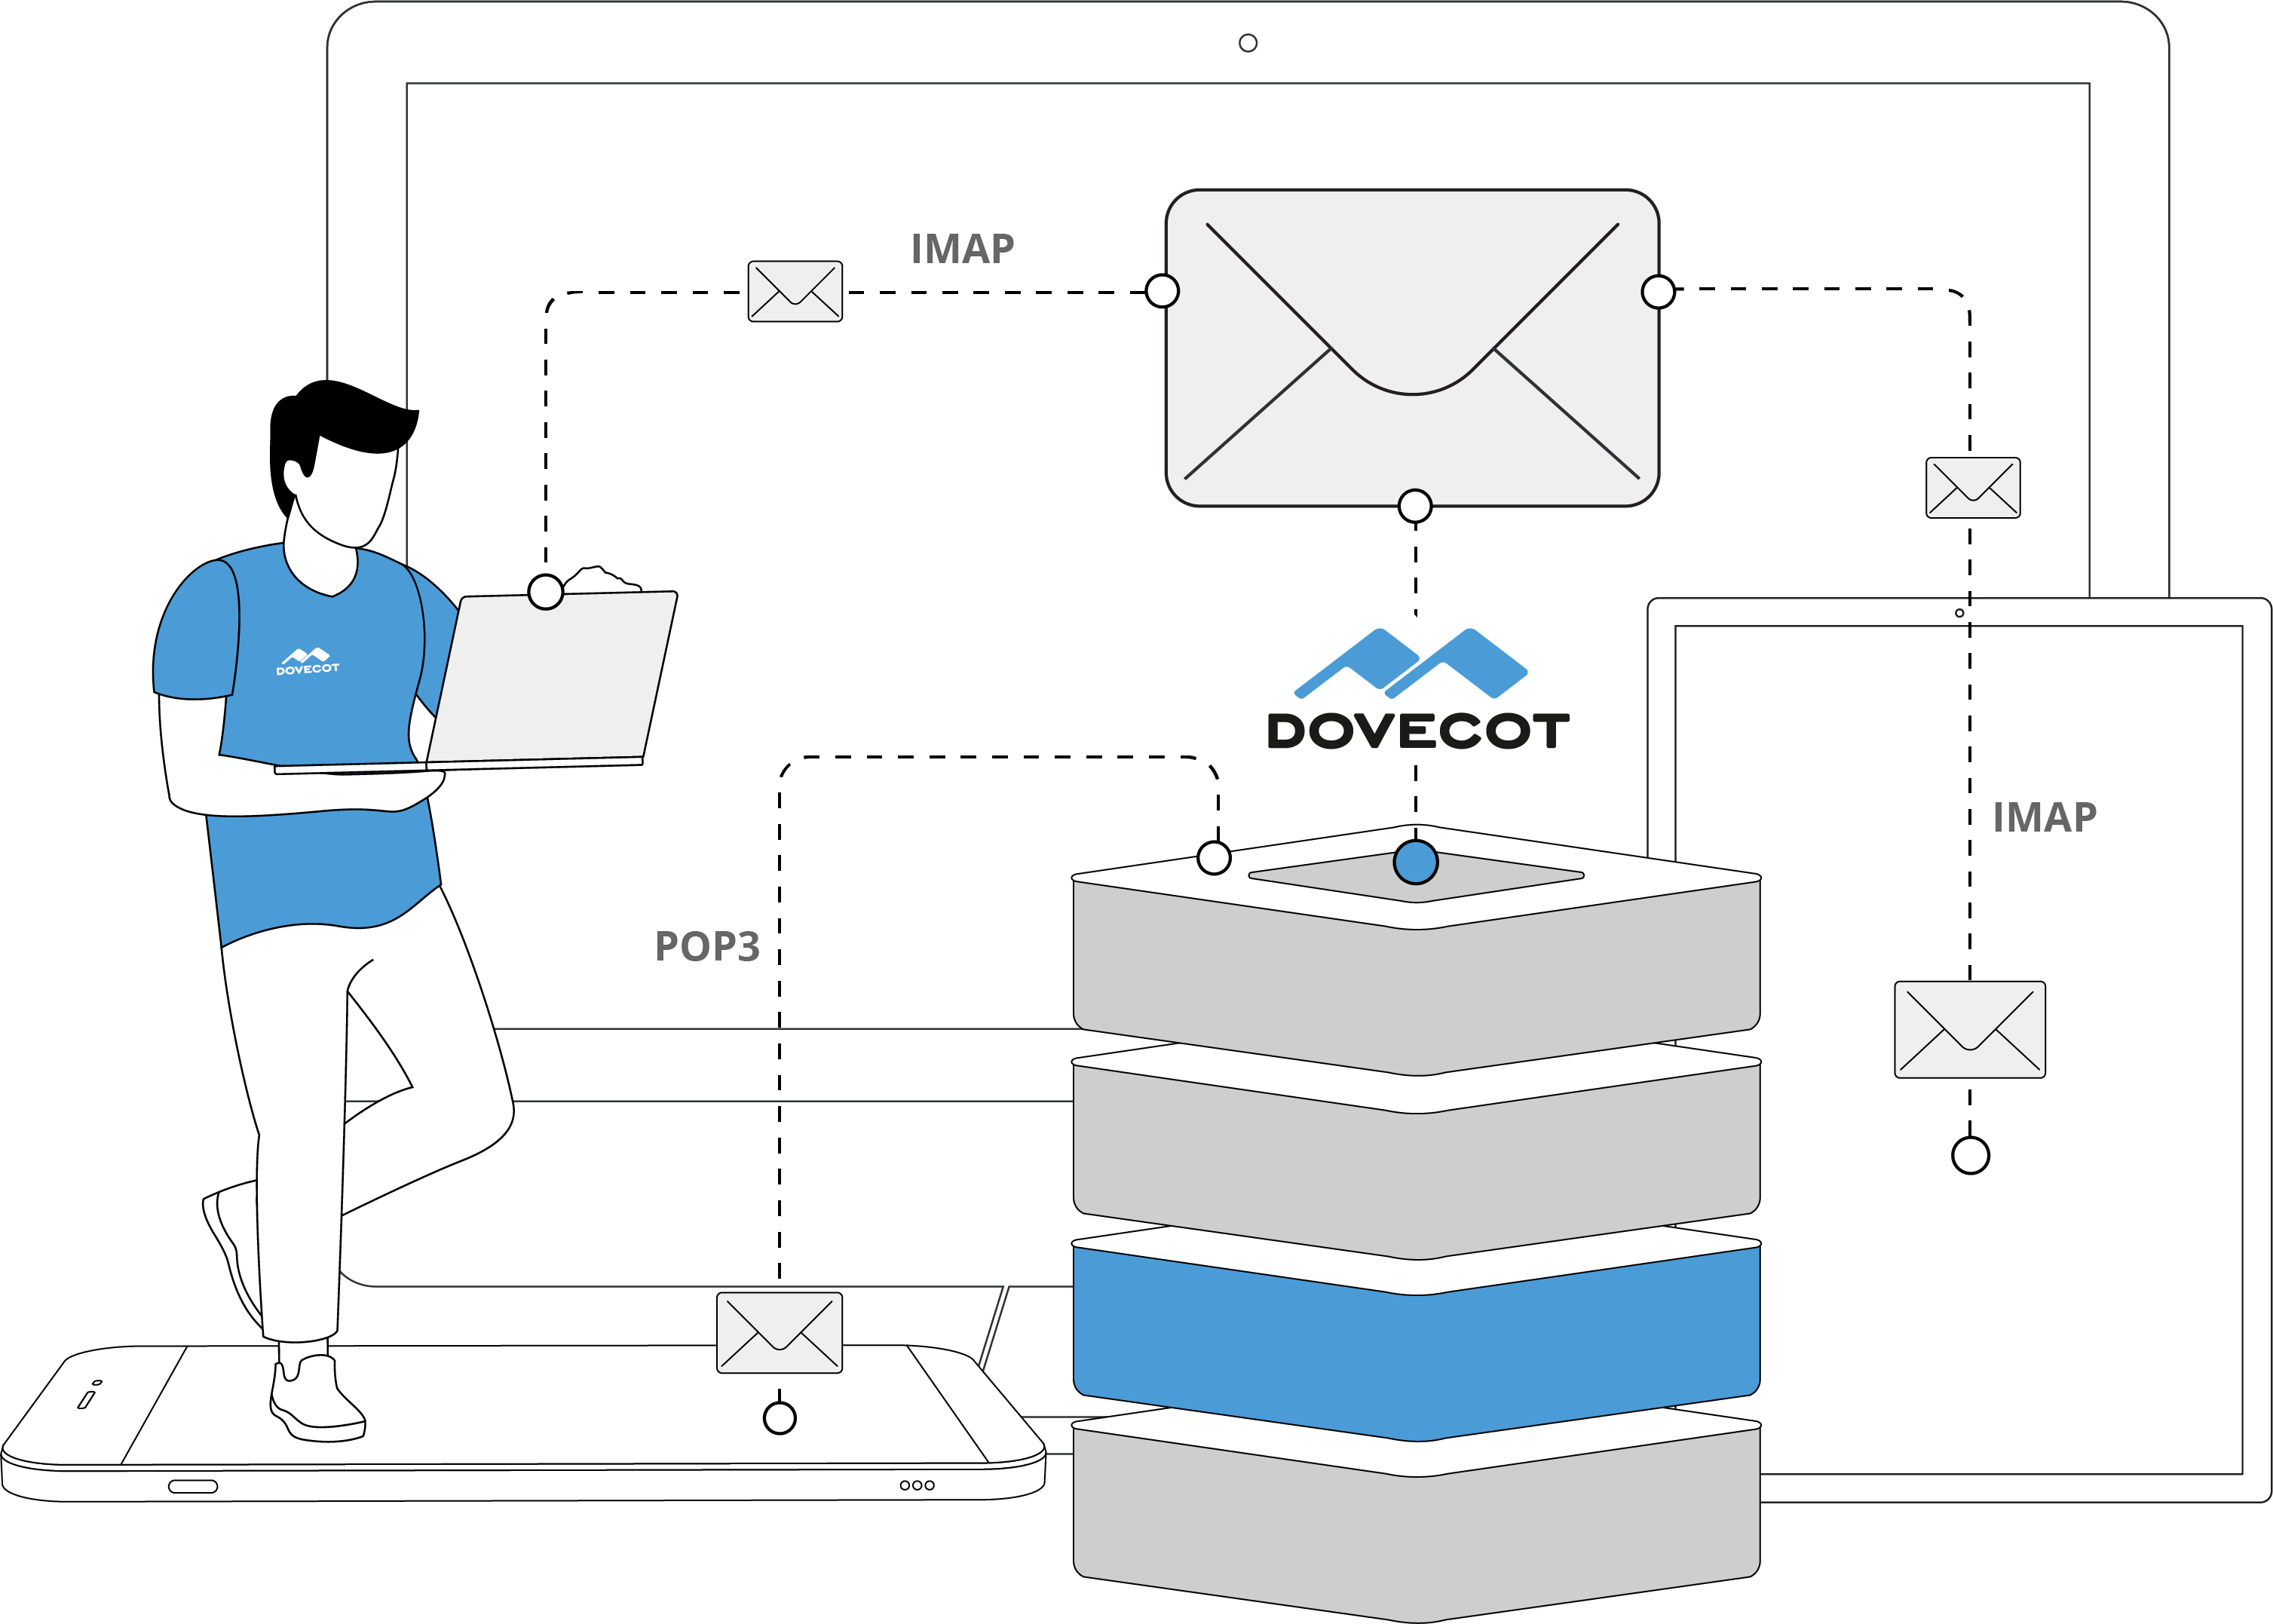
When revamping our mail server, choosing the software to manage the POP3 and IMAP protocols was just as crucial as choosing the MTA server. In this regard, we reaffirmed our trust in Dovecot, which has long been a market leader for efficient and secure email access management. Dovecot was chosen over alternative solutions like Courier primarily for its reliability, flexibility, security , and the wide range of advanced features it offers, particularly regarding security and performance optimization.
One of the key aspects that strengthened our decision to retain Dovecot was its compatibility and integration with the MySQL backend via the dovocot-mysql plugin. This feature allowed us to leverage the same database already used by Postfix, facilitating unified and consistent management of users, quotas, and many other configurations related to both receiving and sending mail. The ability to query the database during login or when managing user quotas through Dovecot represents a significant advantage in terms of operational efficiency and security.
Having already prepared the queries in the old system and the possibility of reusing them without significant changes made Dovecot the ideal solution for our environment. This ensured smooth integration and minimized configuration efforts, allowing us to focus on optimizing and securing the service.
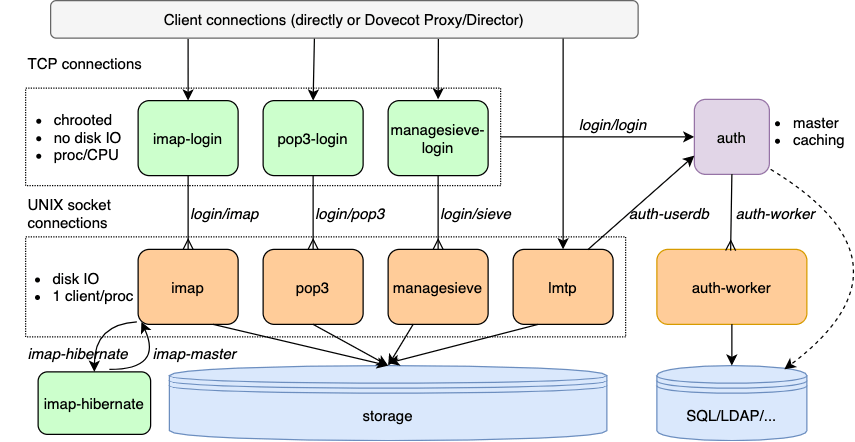
Dovecot natively supports the POP3 and IMAP protocols, including their secure encrypted versions (POP3S and IMAPS), with TLS encryption support. This ensures that all communications between email clients and the server are secure, preserving the confidentiality and integrity of the exchanged data. Dovecot's implementation, combined with advanced security policies and encryption best practices, allows us to offer our users secure access to their email inboxes, minimizing the risks associated with interception and cyber attacks.
Improve the SPAM and security aspect.
While our mail system configuration—with MySQL as the backend, Postfix as the Mail Transfer Agent (MTA), and Dovecot for POP3 and IMAP—might seem complete in theory, everyday reality presents us with ever-new security and SPAM management challenges . These issues represent a constant game of cops and robbers, in which spam attacks and security threats are constantly evolving, requiring ongoing adaptation and attention.
In addressing these challenges, we have chosen to maintain some best practices from the old mail system, replacing or adding components where necessary, to further strengthen our infrastructure against external threats. One of the most effective strategies we have implemented concerns the control of incoming traffic through the main DNSBL lists (DNS-based Blackhole List).
1. Control over master DNSBL lists
DNSBL lists are used to identify and block IP addresses known to be sources of SPAM or other malicious activity. By integrating these lists into our Postfix MTA, we can reject connections from compromised IP addresses upstream. Specifically, we configured Postfix to query the following DNSBL lists :
bl.spamcop.net
b.barracudacentral.org
zen.spamhaus.org
When a message is sent to our server, Postfix automatically checks whether the sender's IP address is on one of these lists. If the IP is listed, the message is rejected before it can enter our system. This preemptive approach has the dual benefit of improving security by filtering out malicious actors before they reach users' inboxes, and optimizing resource usage by preventing the system from using CPU and memory to analyze and handle potentially malicious messages.
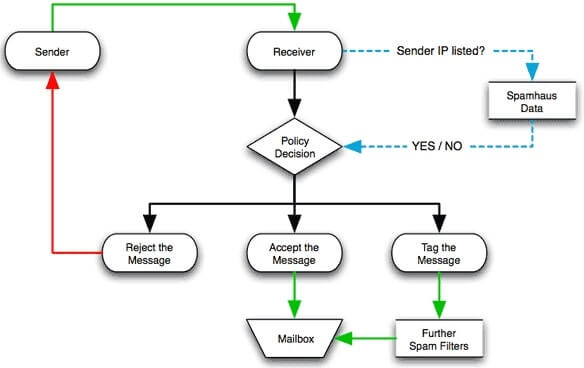
Filtering messages upstream, rejecting connections from blacklisted IP addresses, allows us to significantly reduce the volume of SPAM and threats that manage to penetrate our system. This not only improves the experience of users, who find themselves having to deal with fewer unwanted messages, but also helps maintain the integrity and performance of our mail server, guaranteeing a more secure, reliable and efficient email service.
2. Check the sender's SPF and DKIM
Particular attention was paid to verifying the integrity and authenticity of incoming messages by checking the SPF (Sender Policy Framework) records and the DKIM (DomainKeys Identified Mail) signatures of the senders. These two mechanisms play a crucial role in ensuring that emails received are legitimate and have not been altered or sent by fraudulent entities.
Check SPF
The SPF check allows you to check whether the IP address of the server that sent the email is authorized by the sender's domain to do so. This is achieved by comparing the IP with the list of authorized addresses published in the DNS of the sending domain in the form of an SPF record. If the check fails, this indicates that the email may not have been sent by an authorized entity, increasing the likelihood that it was a phishing or spam attempt. By implementing strict SPF control, we strengthen our defense against email abuse, limiting the possibility of malicious or unauthorized messages reaching end users.
Check DKIM
At the same time, DKIM check adds an additional layer of security by verifying that the content of the email has not been modified during transport. This is achieved by verifying a digital signature attached to the message, which has been generated using a private key known only to the sending domain. The corresponding public key, published in the domain's DNS, is used to decrypt the signature and confirm the integrity of the message. A valid DKIM signature is a strong indicator that the email is authentic and that the content has not been altered, providing users with greater security in managing their email communications.
3. ClamAV and Amavis as Antivirus and Antispam solution
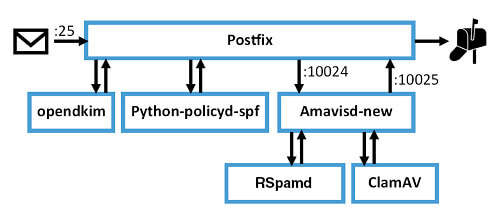
As part of our constant commitment to guarantee the security and integrity of the company email system, we have decided to continue using ClamAV and Amavisd-New, solutions already implemented in our previous mail server. These applications, configured to work together as a Milter (Mail Filter) for Postfix, represent the first line of defense against a wide range of cyber threats, including viruses, malware and spam, which attempt to infiltrate email communications on a daily basis.
What is ClamAV?
ClamAV is an open-source antivirus program specifically designed to detect Trojans, viruses, malware, and other malicious threats in email systems . Thanks to its constantly updated community-generated virus signature database, ClamAV provides timely and effective protection against the latest known threats. Its integration with the mail server allows for real-time scanning of attachments and the contents of incoming and outgoing emails, blocking the spread of malicious content before it can reach recipients or be sent by our users.
What is Amavis (Amavisd-New)?
Amavisd-New, commonly known as Amavis, is a content filter that acts as an interface between your email server and various spam and virus checking tools, including ClamAV. Amavis analyzes messages in transit, leveraging the detection capabilities of ClamAV and other anti-spam tools to evaluate the legitimacy and safety of the content. In addition to virus scanning, Amavis implements checks based on blacklists, heuristic analysis and Bayesian filters to effectively identify and manage spam messages.
The ClamAV and Amavis combination on the mail server
The collaboration between ClamAV and Amavis on our email server constitutes an integrated and highly effective anti-spam and anti-virus system. While ClamAV focuses on detecting and neutralizing viral threats, Amavis acts as a powerful content filter, examining every message for spam and malware using a series of advanced techniques. This multi-layered approach to security allows us to intercept a wider range of threats, ensuring overall protection of our email communication system.
Configuring ClamAV and Amavis as a Milter filter for Postfix allows you to tightly integrate spam and virus scanning capabilities directly into Postfix's message processing flow, thus optimizing performance and minimizing the impact on email delivery time. This solution not only significantly improves the security of our mail server, but also helps maintain user trust by ensuring that their communications are protected from a wide range of cyber threats.
4. Rspamd as a high-performance alternative to the obsolete SpamAssassin
Again with the aim of obtaining the maximum in terms of antispam, we decided to adopt Rspamd to replace SpamAssassin, which we had used in our previous mail server. This choice was driven by the need to respond more effectively and quickly to the sophisticated strategies used by modern spammers, while ensuring minimal impact on system resources.

Why Rspamd?
Rspamd stands out as a modern, high-performance spam filtering solution. Unlike SpamAssassin, known for its rule-based approach and flexibility, Rspamd introduces numerous improvements in processing speed, spam detection accuracy, and reduced resource consumption.
Thanks to its modular architecture and native support for multiprocessing, Rspamd is able to analyze a significantly greater volume of messages in parallel, reducing waiting times and improving the end-user experience.
Advanced features and integration with REDIS
One of the most appreciated features of Rspamd is its ability to integrate with external systems such as REDIS, an in-memory data store that can be used to store various types of data useful for spam filtering, such as message fingerprints, blacklists/whitelists and Bayesian scores. This integration allows Rspamd to offer advanced features such as rate limiting, real-time metric-based greylisting and sending pattern control, significantly improving the system's resilience to spam and phishing attacks.
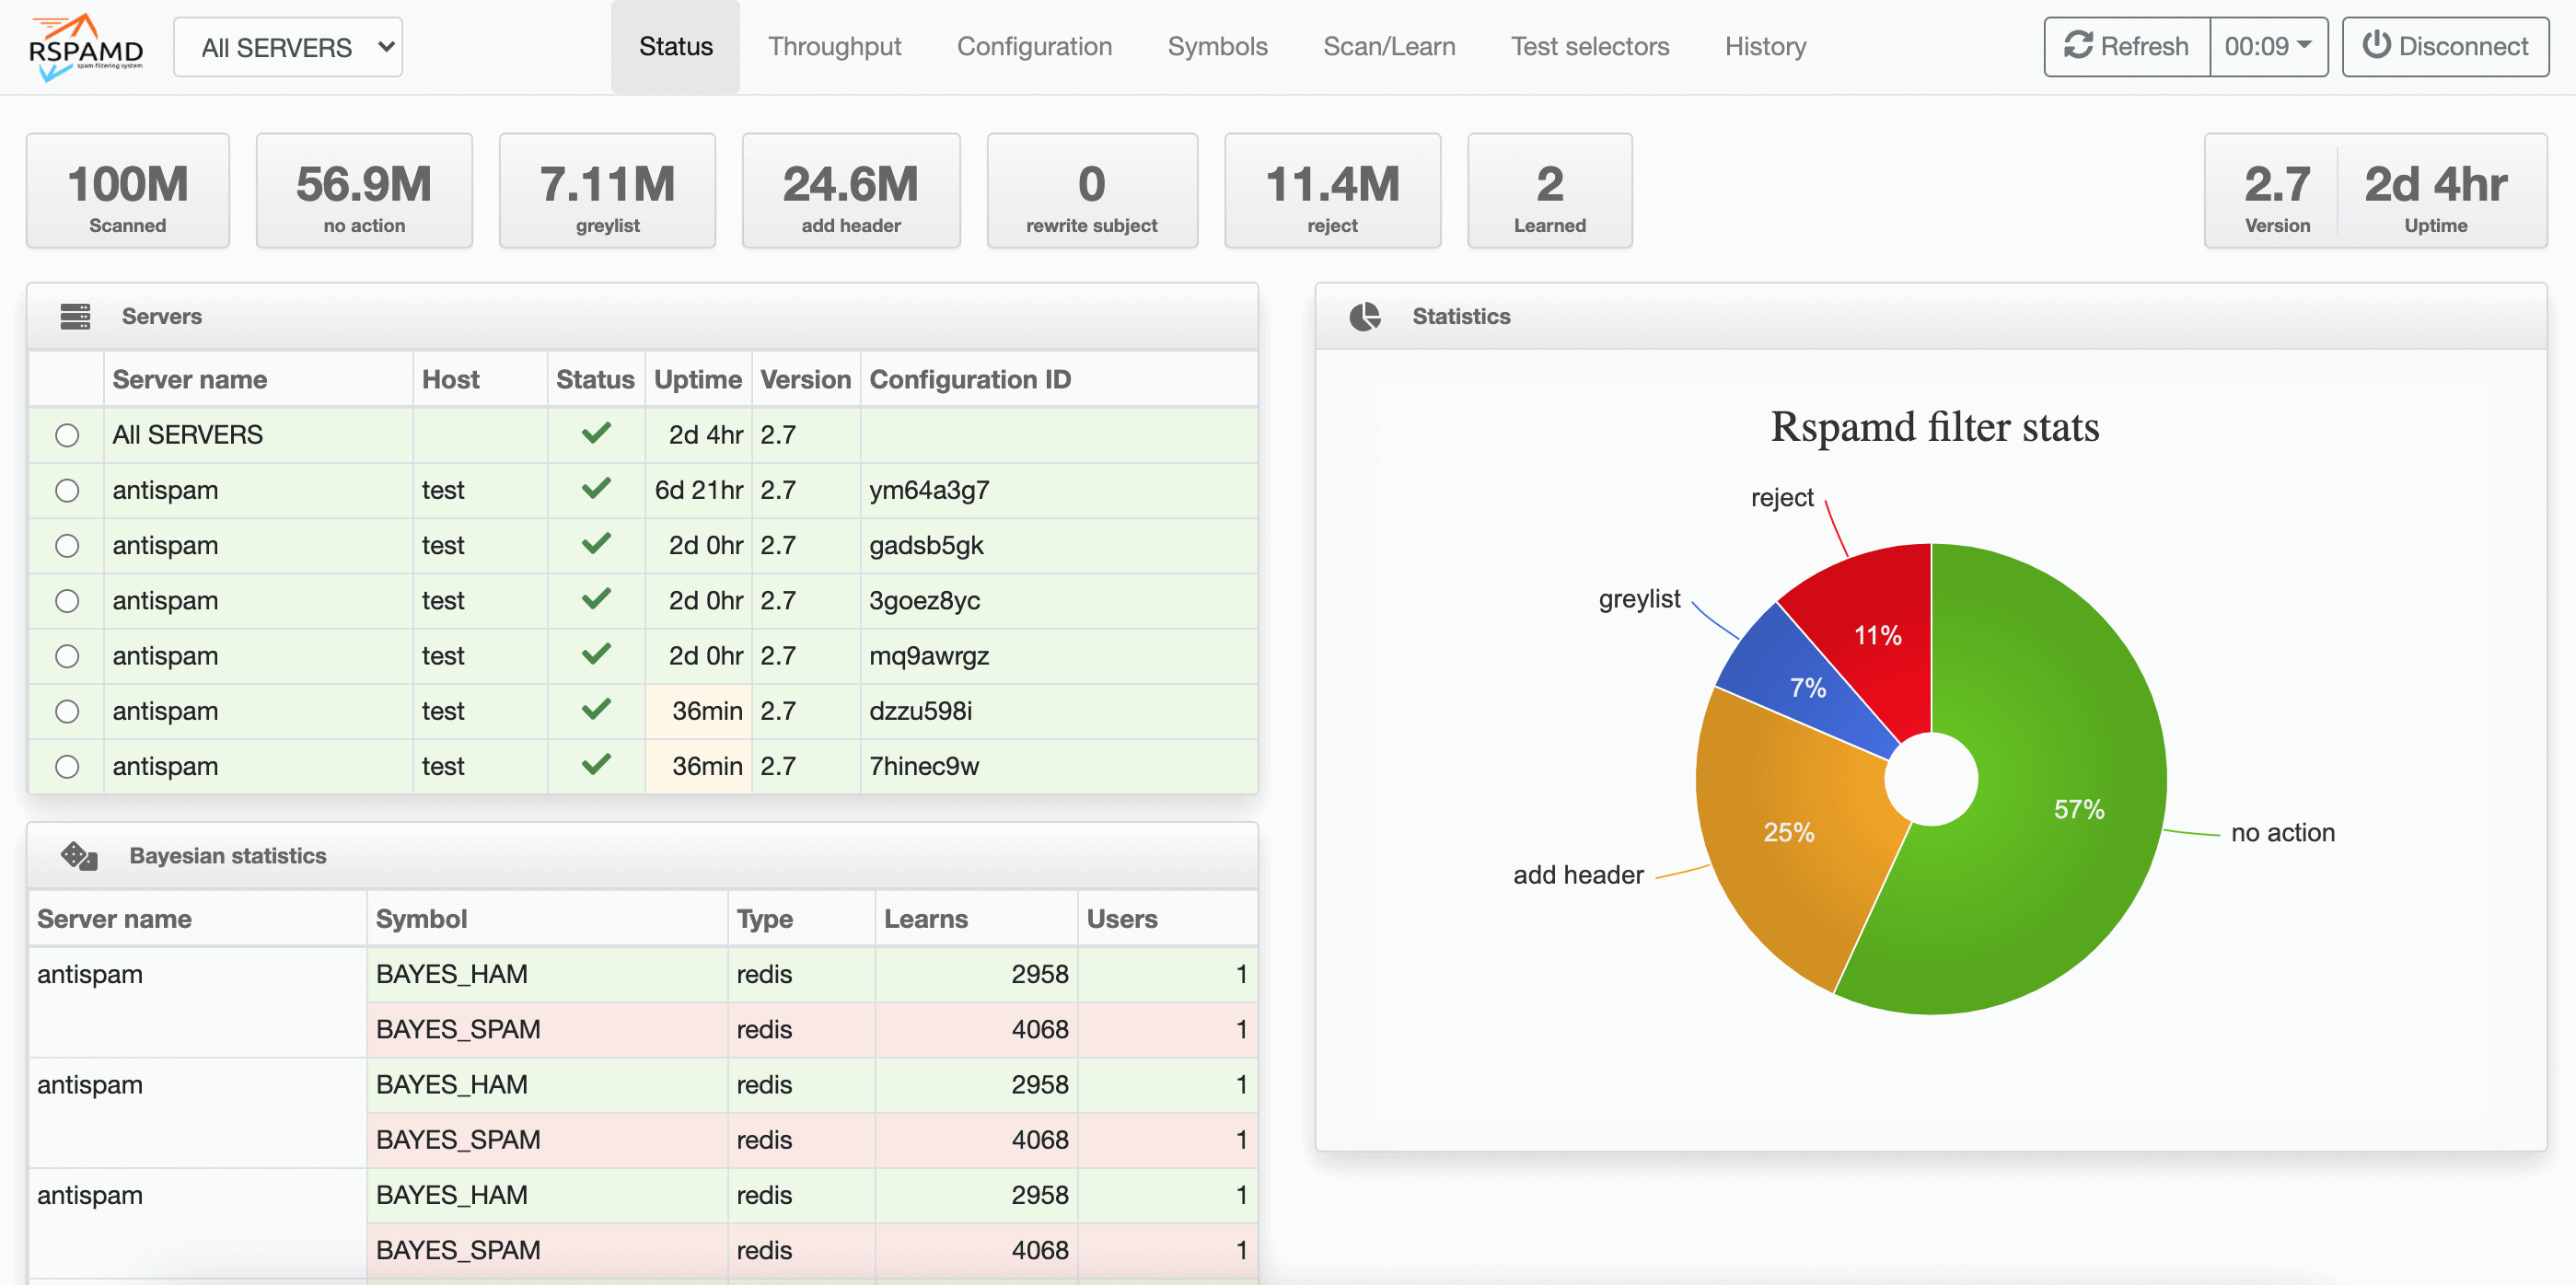
Additionally, Rspamd has a rich and evolving set of modules for content analysis, DKIM (DomainKeys Identified Mail) checking, SPF (Sender Policy Framework), DMARC (Domain-based Message Authentication, Reporting & Conformance), and phishing detection. These tools, combined with machine learning algorithms, allow Rspamd to dynamically adapt to new spamming techniques, offering proactive protection against emerging threats.
Better performance and scalability
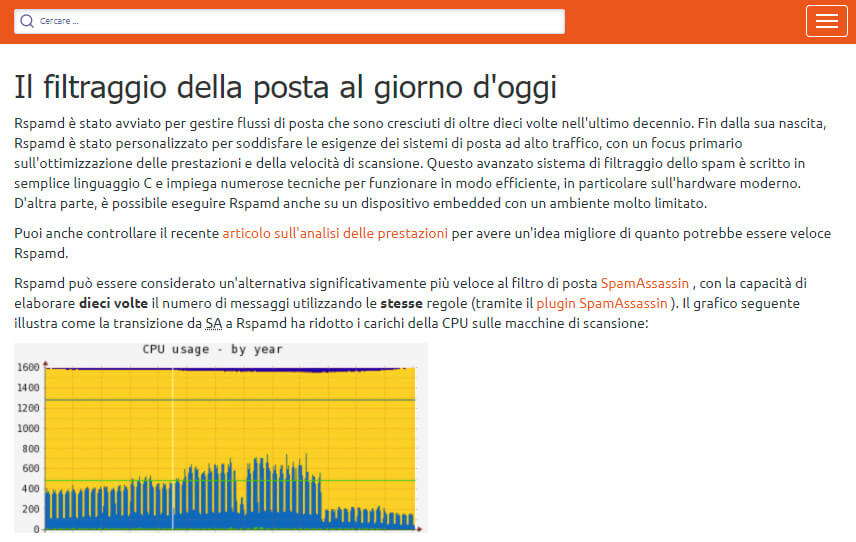
Migrating to Rspamd has resulted in a significant improvement in the overall performance of our spam filtering system. Its efficiency in message processing has made it possible to reduce workloads on servers, ensuring faster response times and greater system scalability. This is particularly relevant in the context of a growing demand for secure and reliable email services, where the ability to handle large volumes of traffic without compromising quality of service is crucial.
5. Implement policyd-spf to control SPF policies
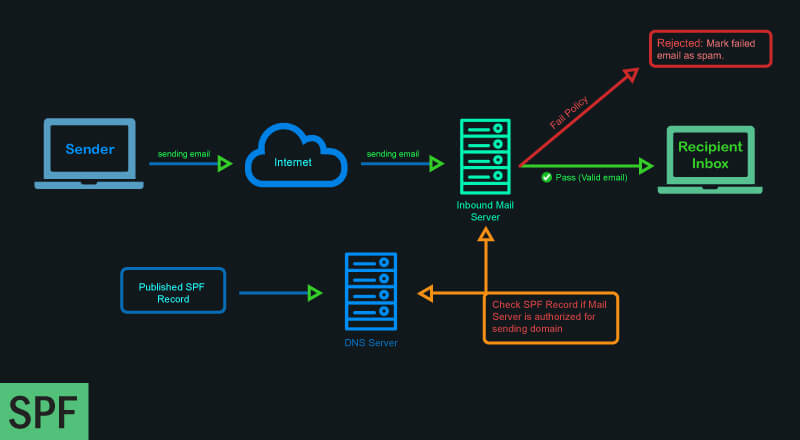
In our ongoing effort to strengthen the security and integrity of the corporate email system, we have integrated policyd-spf, a specific tool for implementing and controlling SPF (Sender Policy Framework) policies. This decision is part of the broader strategy to adopt cutting-edge security practices to prevent email abuse and fraud, ensuring that only authorized senders can send messages on behalf of the domain.
What is SPF and why is it important?
SPF is an email validation method designed to prevent sender spoofing, a fraudulent activity in which an attacker sends emails by making the message appear to come from a different domain than the one actually used. By publishing an SPF record in the domain's DNS, administrators can specify which mail servers are authorized to send emails on behalf of their domain. When a receiving server gets an email, it can check the SPF record of the sending domain to see if the server that sent the email is actually authorized to do so.
The implementation of policyd-spf
Policyd-spf was chosen for its ability to integrate seamlessly with Postfix as a policy service, allowing real-time SPF checks during the email receiving process. When an email arrives, policyd-spf consults the SPF record of the sending domain to determine whether the sending server's IP address is authorized. If the check fails, the message can be rejected or reported according to configured policies, significantly helping to reduce the risk of receiving fraudulent or spam emails.
Advantages of using policyd-spf
Adopting policyd-spf offers numerous email security benefits:
Reduce Spam and Phishing: By effectively implementing SPF controls, we decrease the likelihood of unauthorized emails reaching end users, reducing the risk of phishing and spam attacks.
Improving domain reputation: By ensuring that only authorized messages are sent on behalf of our domain, we maintain and improve the domain's reputation in the eyes of spam filters and receiving mail servers.
Compliance and reliability: Using policyd-spf helps ensure compliance with modern email security standards, helping to build a more secure and reliable email ecosystem.
6. Implementation of DKIM control with dkim-milter
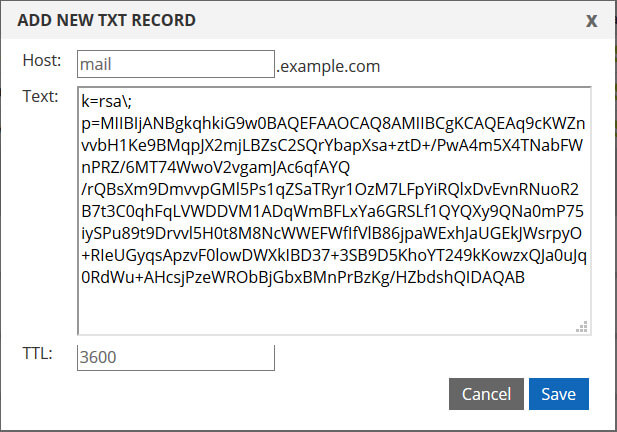
To address the challenges posed by sophisticated spam and email fraud strategies, we have implemented dkim-filter as an essential component of our email security system. This tool, configured as a milter (mail filter) for Postfix, plays a vital role in strengthening our anti-spam defenses by checking DKIM (DomainKeys Identified Mail) records of incoming and outgoing emails.
What is DKIM and why is it important?
DKIM is an email authentication standard that allows the recipient to verify that an email sent in their name actually comes from the domain that claims to be the sender. This is achieved by digitally signing messages with a private key from the sending domain; the corresponding public key is published in the domain's DNS. Mail servers receiving the email can then verify the signature using the public key, ensuring that the contents of the message have not been altered during transport and confirming the authenticity of the sender.
The dkim-filter utility
Dkim-filter acts as an interface between the email server and the DKIM signing/verification process, providing an efficient mechanism for applying and validating DKIM signatures. When configured as a milter for Postfix, dkim-filter automatically signs outgoing emails with the private key of the sending domain and verifies the signatures of incoming emails against the public keys published by the sending domains.
This dual functionality not only significantly improves anti-spam control by verifying the authenticity of received messages, but also helps build and maintain the domain's reputation as a reliable sender. In an environment where phishing attacks and other forms of email abuse are commonplace, implementing DKIM through dkim-filter provides an additional security measure that helps protect both the sender and recipient from potential harm .
Advantages of adopting dkim-filter
- Improved spam filtering: By validating DKIM signatures, dkim-filter helps effectively filter unauthenticated emails that could be spam or phishing attempts.
- Increased deliverability: Emails sent from our domain with a valid DKIM signature are more likely to pass recipients' spam filters, thus improving the deliverability of our communications.
- Domain identity protection: By providing a reliable way to authenticate messages, dkim-filter helps protect our domain identity, preventing spoofing and strengthening users' trust in the emails they receive.
7. Implementation of Fail2Ban to limit login attempts and bruteforce attacks.
To effectively counteract bruteforce attacks and limit unauthorized login attempts, our mail server is equipped with Fail2Ban, an essential security tool for Linux hosting and systems. Fail2Ban is an application that monitors service logs to identify suspicious behavior, such as repeated failed login attempts, a potential sign of a bruteforce attack. Once a pattern of failed logins is detected, Fail2Ban intervenes by blocking the source IP address via firewall rules, thus preventing further attempts for a defined period of time.
The adoption of Fail2Ban represents a preventive measure against security risks and threats that can compromise the integrity and availability of the server. Bruteforce attacks, in addition to targeting unauthorized access, can in fact degenerate into Denial of Service (DDoS) attacks, overloading the server with incessant requests that occupy critical resources such as RAM and CPU, resulting in slowdowns or interruptions of service.
When configuring our mail server, we implemented a balanced security policy for POP3, IMAP, and SMTP email services. After 6 incorrect login attempts, the source IP is automatically blacklisted for one minute. This approach allows us to limit login attempts to 360 per hour, effectively balancing the need to protect the server from brute-force attacks with the ability to grant legitimate users, who may have simply forgotten their credentials, the opportunity to retry without incurring prolonged blockages.
Additional policies for sending via rate limit, DKIM signing and specific queue management.
In addition to everything listed so far, we have implemented a series of additional policies regarding the rate limit of sendings, the application of the DKIM signature and personalized management of outgoing message queues. These measures have been taken to ensure a reliable, secure email service in line with industry best practices.
Implementation of Rate Limit for Authenticated Senders
To prevent abuse of the email system, such as compromised accounts used to send spam or phishing attacks, we have introduced a rate limit for authenticated senders. This limit has been set at 1000 emails per day per single sender, a number deemed adequate for legitimate use by corporate and individual users. This policy aims to limit the potential damage in the event of a compromise by preventing our mail server from being blacklisted due to sending excessive volumes of unauthorized email.
Applying DKIM Signature to All Outgoing Emails
Another pillar of our email security strategy is the universal implementation of DKIM (DomainKeys Identified Mail) signature for all outgoing emails handled by our mail server. The DKIM signature provides an authentication method that helps receiving servers verify that the email was actually sent from the domain that appears in the sender field, helping to improve deliverability and protect the reputation of our domains. To facilitate this process, each domain needs to insert the corresponding DKIM public key into its DNS in the form of a TXT record.
Personalized Management of Outgoing Queues
Recognizing the different policies and limitations imposed by major email service providers, such as Microsoft, Google, Yahoo, and Italian providers like Telecom, Tiscali, and Libero, we have developed a flexible and customized policy for managing outgoing message queues. This approach includes using different IP addresses for sending and applying specific "throttling" speeds for each operator, based on their requests and policies. This strategy allows us to maximize the use of our IP range while avoiding excluding IP addresses from use simply because they might be blacklisted by a single provider.
This malleable policy of managing queues and sending IPs gives us the flexibility to quickly adapt to changing network conditions and email service provider policies, while ensuring that our communications are delivered efficiently and without interruptions. By implementing these measures, we not only improve the security and reliability of our email service, but also ensure that our users' emails reach their recipients as intended, maintaining effective and professional business communication.
AJAX webmail via Roundcube, a de facto standard.
Regarding solutions for web-based access to email, we have chosen to continue to propose and use Roundcube, an AJAX-based webmail interface that has established itself as a de facto standard among hosting providers. This decision reflects our commitment to providing users with an email experience that is intuitive, feature-rich, and easily accessible from any web browser.
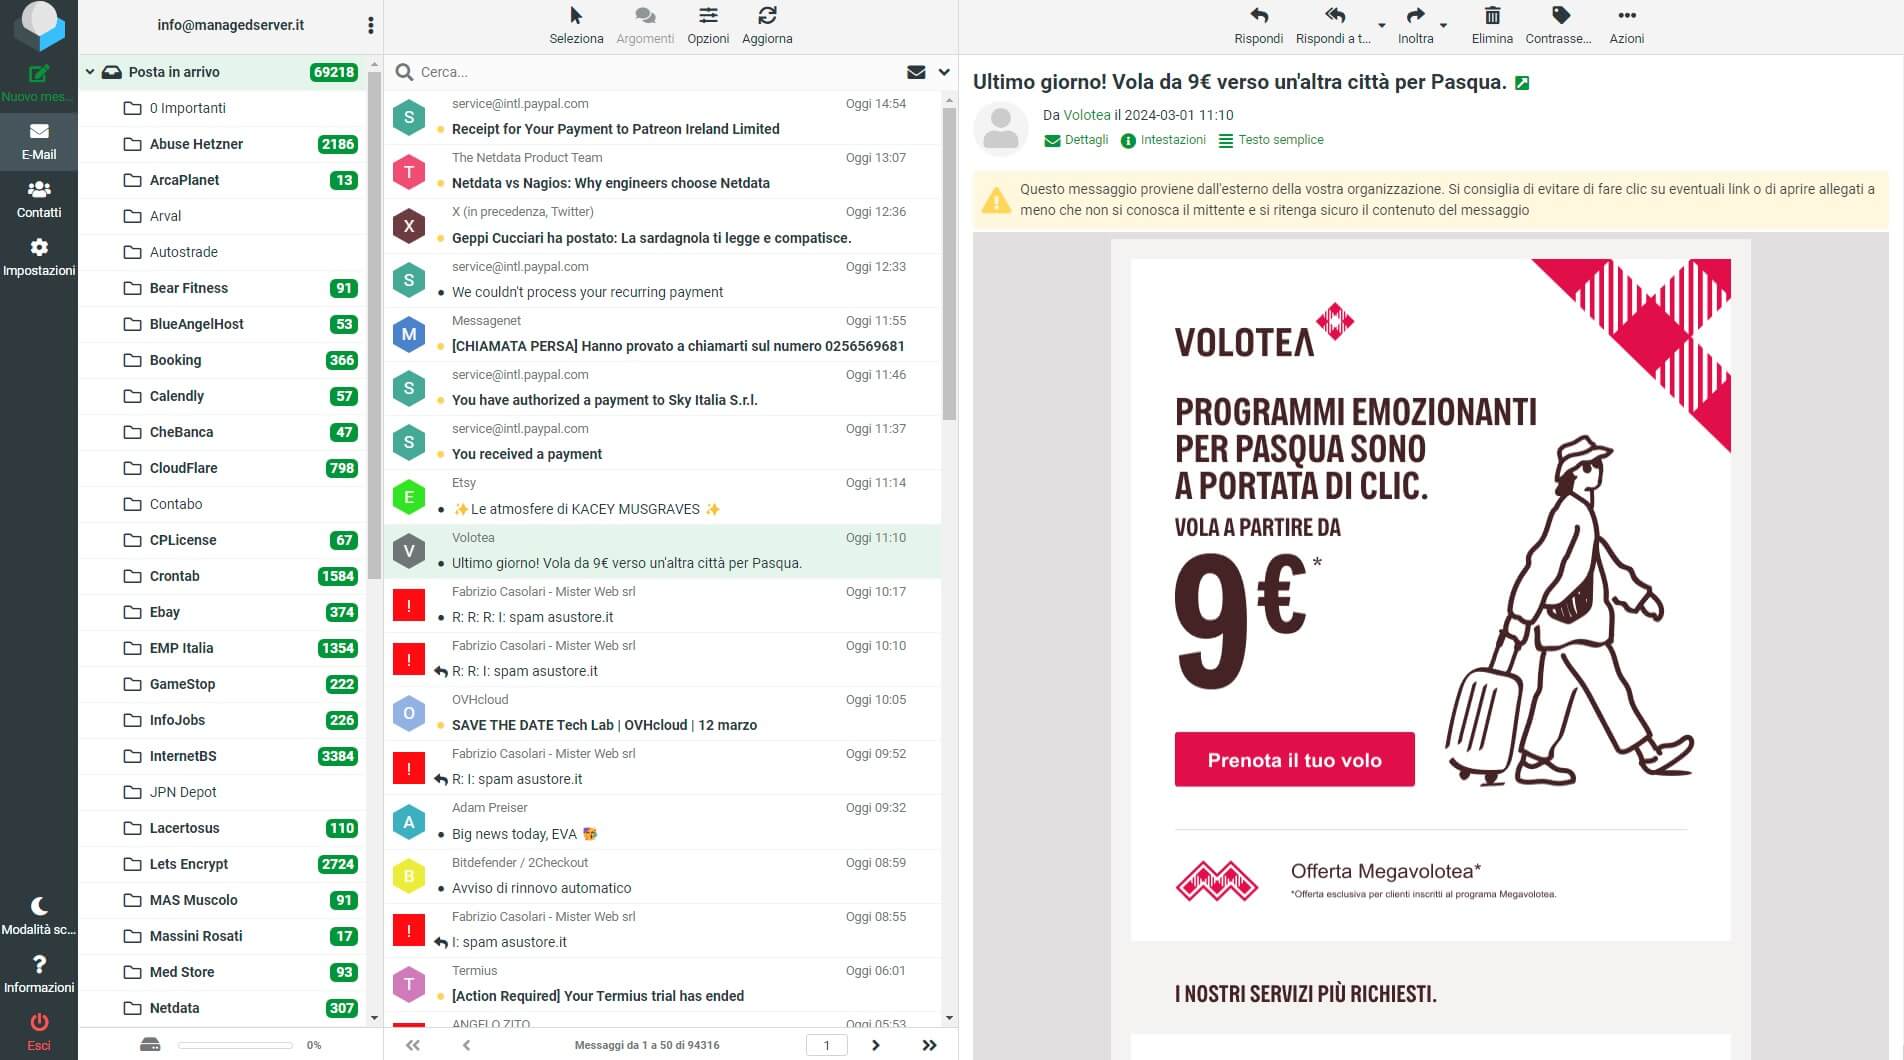
Roundcube is an open source webmail application that allows users to read, send and organize emails directly from a web browser, without the need to set up a separate email client. Thanks to its AJAX-based user interface, Roundcube offers an experience similar to that of a desktop application, with fluid and responsive operations, such as dragging messages between folders, instant search and advanced contact management.
Roundcube integrates seamlessly with our Dovecot IMAPS server and Postfix mail system, offering a complete and seamless email management solution. With Dovecot, Roundcube users benefit from secure and high-performance access to their email inboxes, leveraging encrypted protocols like IMAPS for maximum data security. Furthermore, Postfix compatibility ensures that sending and receiving email through Roundcube is reliable and efficient, with support for advanced features like DKIM signing and SPF checking for greater security and reliability of sent messages.
Adopting Roundcube as a webmail interface offers numerous advantages for both end users and system administrators. Users appreciate its clean and intuitive interface, the wide range of email management features, and the ability to customize the experience to their needs. Administrators, for their part, benefit from Roundcube's ease of installation and configuration, its extensive documentation, and the support of an active and dedicated community.
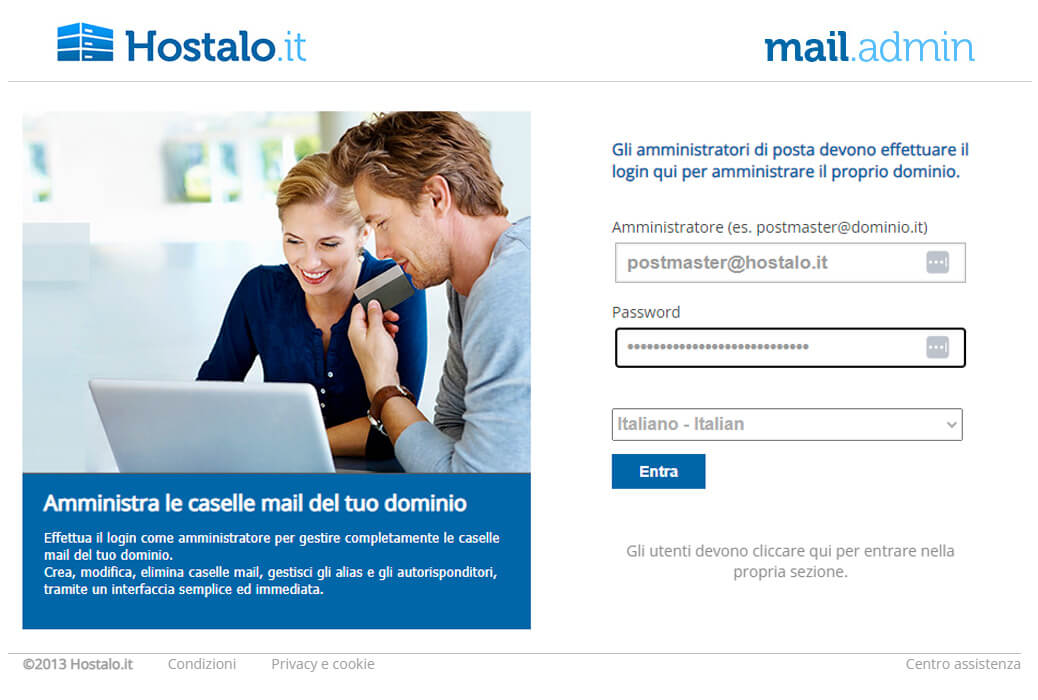
We have obviously completely revised the front end, providing the interface with a more aesthetically appealing and functional Login screen , integrating information and links for users who need to not only use the Webmail, but also perform operations such as alias management, password reset, autoresponder and similar.
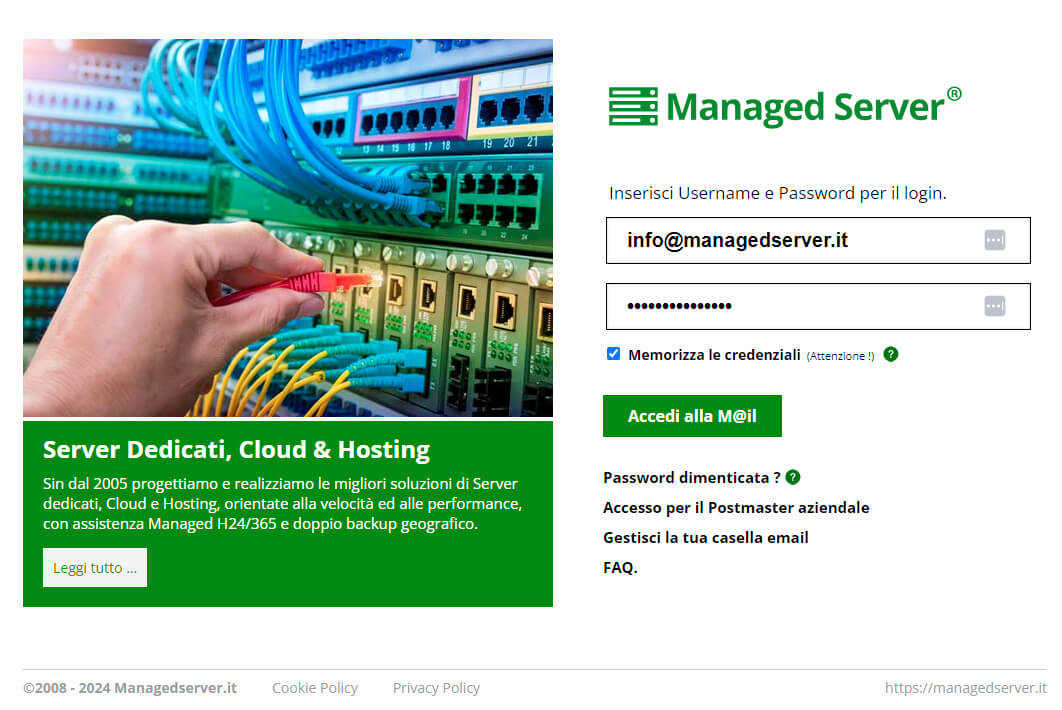
Among the features, which are not just aesthetic, are a slider that allows you to illustrate the various services we provide at Managed Server Srl, and a related button that leads to external links such as pages on our website, and a function for storing credentials using a cookie . Among other things, we have also added a Cookie Consent and Privacy Policy and Cookie Policy using the Iubemda service.
Backup and Disaster recovery
In the context of our email system infrastructure, resilience and disaster recovery are top priorities. While we have implemented a CEPH-based system, known for its high reliability and triple replication capability, we have gone further in building a comprehensive approach to backup and disaster recovery that spans both system and data.
Bare Metal Backup Daily
Regarding the mail server system, we have implemented a bare metal daily backup strategy, using snapshots. This approach allows us to fully capture the state of the system at regular intervals, ensuring that in the event of severe system failures or corruptions, we can quickly restore the entire environment to previously captured operating conditions. Bare metal snapshots provide a complete backup solution that includes the operating system, applications, configuration and data, offering robust security against critical data loss.
Redundant Backup of CEPH Storage Data on double Geographic SAN
For data storage, which leverages the CEPH infrastructure, we take an even more rigorous and layered approach to backup. We carry out two separate backups daily, using two different software technologies: Borg and Restic, operating via RClone. These backups are performed on two geographically separate Storage Area Networks (SANs), one located in Germany and the other in Finland, to maximize redundancy and minimize the risk of data loss following catastrophic events or hardware failures.
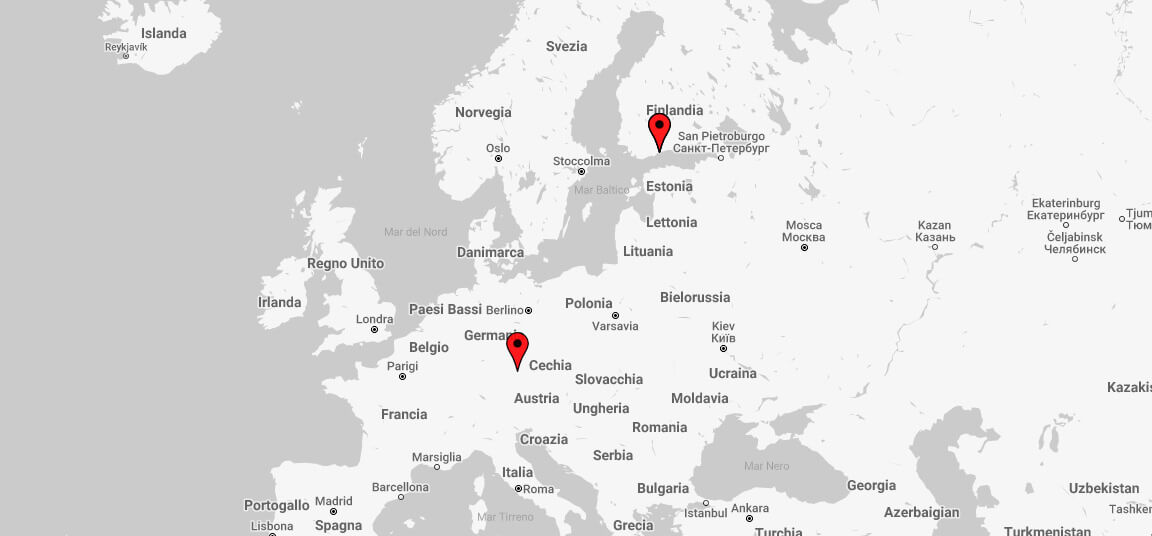
Using two different backup technologies allows us to leverage the unique strengths of each, increasing the overall resilience of our backup system. Borg is known for its efficiency in data deduplication, reducing the space needed for backups, while Restic offers great flexibility and speed in data recovery. Operating via RClone, both backup systems ensure secure and reliable transfers to remote SANs.
Redundancy and Data Retention
The SANs on which backups are performed are configured in RAID 10, combining data redundancy with high read and write performance. This configuration, combined with our choice to use two distinct backup technologies and the diversified geographical location of the SANs, allows us to confidently face disaster recovery scenarios, ensuring operational continuity even in the most critical situations.
We implement a 60-day data retention policy, which allows us to maintain an extensive backup history, increasing our recovery capabilities should the need arise and providing ample time to identify and respond to any data loss.
Conclusion
Our experience building and improving corporate email systems highlights a fundamental truth: the open source world today offers all the components needed to build an advanced, high-performance, and secure email server, without the need to rely on proprietary commercial solutions . By adopting cutting-edge open source technologies such as Postfix, Dovecot, Roundcube, ClamAV, Amavis, and Rspamd , as well as employing advanced backup systems and security policies such as DKIM and SPF, we have succeeded in building an email infrastructure that not only meets our users' security and reliability needs but does so with significantly greater cost-effectiveness than commercial alternatives.
This choice has allowed us to benefit from unparalleled flexibility in customizing and optimizing the system, while ensuring that each component is updated and maintained in line with best security and performance practices. The open source ecosystem, with its vast community of developers and IT professionals, offers a level of support and continuous innovation rarely found in closed, proprietary solutions.
Furthermore, the cost savings resulting from the use of Open Source software not only translates into an immediate economic advantage but also allows resources to be reinvested in other critical areas of the IT infrastructure, such as data security, disaster recovery and innovation technological, thus contributing to further improving the quality of the service offered to end users.
In conclusion, our experience confirms that Open Source software represents a precious and strategic resource for the development of advanced and high-performance email systems. The ability to provide a complete, secure and cost-efficient solution underlines the value of Open Source as a foundation on which to build and expand modern IT infrastructures, dispelling the myth that only proprietary commercial solutions can guarantee high levels of efficiency and security.
After 5 days, not a single user has had post-migration access problems.
If you, your company or your organization are also looking for a highly technological custom solution for complete mail management, please contact us.

